Navigating the Digital Frontier: Mastering the SSH Command with Custom Ports
In the sprawling, interconnected landscape of digital infrastructure, Secure Shell (SSH) stands as a foundational pillar, enabling secure remote access and management of servers and network devices. For system administrators, developers, and cybersecurity professionals alike, SSH is an indispensable tool, facilitating encrypted communication over unsecured networks. While its default operation on port 22 is widely understood, the ability to specify a custom port for SSH connections represents a critical, often overlooked, layer of flexibility and security.
This deeply comprehensive guide delves into the nuances of using the SSH command with a custom port, dissecting not only the fundamental syntax but also exploring the profound implications for security, network architecture, and operational efficiency. From the strategic advantages of moving beyond the default to advanced configuration techniques and essential security best practices, we will navigate the digital frontier to empower you with mastery over your SSH connections.
The Ubiquitous Nature of SSH and the Default Port 22
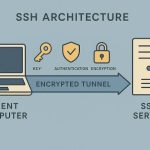
Before venturing into custom port configurations, it’s essential to understand the bedrock of SSH itself. SSH is a cryptographic network protocol that allows secure data communication, remote command-line login, and other secure network services between two networked computers. It provides strong authentication and encrypted data communications between two computers connecting over an open network, such as the internet.
Why Port 22 Became the Standard
When the SSH protocol was first standardized, port 22 was officially assigned to it by the Internet Assigned Numbers Authority (IANA). This designation was a pragmatic choice, providing a well-known endpoint for clients to connect to servers without explicit port specification. The advantages were clear: ease of discovery, simplified configuration, and broad compatibility across diverse operating systems and network devices.
However, this very ubiquity presents a double-edged sword. While convenient, the universal knowledge of port 22 as the SSH entry point also makes it a primary target for automated scans, brute-force attacks, and malicious probing by threat actors. Every day, countless bots scour the internet for open port 22 services, attempting to gain unauthorized access.
The “Security by Obscurity” Debate
The concept of using a custom SSH port often intersects with the “security by obscurity” debate. Critics argue that merely changing a port number doesn’t fundamentally enhance security, as sophisticated attackers can still discover the custom port through port scanning techniques. They emphasize that robust security measures, such as strong authentication, firewall rules, and regular updates, are far more critical.
While this perspective holds merit, dismissing custom ports entirely would be an oversight. For the vast majority of automated, unsophisticated attacks – the sheer volume of which can be overwhelming – moving SSH to a non-standard port acts as a highly effective filter. It significantly reduces the “noise” of unsolicited connection attempts, freeing up server resources and diminishing the attack surface against the most common threats. It’s not a standalone security solution, but rather a valuable component within a layered defense strategy.
Strategic Advantages: Why Opt for a Custom SSH Port?
The decision to move SSH from its default port is rarely arbitrary. It’s a calculated maneuver driven by a combination of security enhancements, operational flexibility, and network management considerations.
1. Enhanced Security Through Reduced Exposure
The primary motivation for many administrators is to bolster security. By relocating SSH to a less common port, you immediately become less visible to automated bots and script kiddies who primarily target port 22. This significantly reduces the volume of login attempts and brute-force attacks logged on your server, making it easier to identify genuinely suspicious activity and conserve system resources that would otherwise be consumed processing these illegitimate requests. While a determined attacker can still find your custom port, it raises the bar, forcing them to expend more effort than a simple default scan.
2. Bypassing Network Restrictions and Firewalls
In certain network environments, particularly corporate or public Wi-Fi networks, outbound connections to common ports like 22 might be blocked by firewalls or proxy servers. By configuring your SSH server to listen on a port that is typically open for other services (e.g., port 443, commonly used for HTTPS, or other high-numbered ports), you can sometimes bypass these restrictions, enabling remote access that would otherwise be impossible. This is particularly useful for users connecting from highly restrictive network segments.
3. Running Multiple SSH Services on a Single Host
While less common, there are scenarios where you might need to run multiple SSH daemon instances on the same server, each potentially serving different purposes or user groups with distinct configurations. By assigning each SSH daemon a unique custom port, you can manage these separate services independently without port conflicts. This allows for greater segmentation and control within complex server architectures.
4. Standardization in Complex Environments
In organizations with extensive server farms, standardizing on a range of custom SSH ports (e.g., all development servers use port 2222, all production servers use port 2223) can simplify network management and security policies. It creates clear internal conventions, reducing ambiguity and aiding in the rapid identification of server types based on their SSH port.
The Core Command: Executing SSH with a Custom Port
At its heart, specifying a custom port with the SSH command is remarkably straightforward, involving a single, essential flag: `-p`.
Basic Syntax Explained
The fundamental command to connect to an SSH server listening on a non-default port is:
bash
ssh -p [port_number] [user]@[host]
Let’s break down each component:
- `ssh`: The command-line client for the Secure Shell protocol.
- `-p [port_number]`: This is the crucial flag. The lowercase `-p` followed by the desired port number tells the SSH client to attempt the connection on that specific port instead of the default port 22.
- Important Note: The uppercase `-P` has a different meaning; it’s used for forwarding SSH connections, not specifying the remote port. Always use lowercase `-p` for this purpose.
- `[user]`: The username you want to log in as on the remote server. For example, `root`, `ubuntu`, `ec2-user`, or your custom user account.
- `@`: A separator between the username and the host.
- `[host]`: The hostname or IP address of the remote server you wish to connect to. This could be `example.com`, `192.168.1.100`, or `my-server-alias`.
Practical Examples
Let’s illustrate with some concrete scenarios:
Example 1: Connecting to a Server on Port 2222
Imagine you have a server with the IP address `203.0.113.45`, and you want to log in as the user `admin` to its SSH service, which is configured to listen on port `2222`.
bash
ssh -p 2222 [email protected]
Upon executing this command, your SSH client will attempt to establish a secure connection to `203.0.113.45` specifically on TCP port `2222`.
Example 2: Using a Hostname with a Custom Port
If your server has a friendly hostname, say `dev-server.yourdomain.com`, and the SSH service is on port `8888`, logging in as `developer` would look like this:
bash
ssh -p 8888 [email protected]
Example 3: Specifying an Identity File (SSH Key)
When using SSH key-based authentication (highly recommended!), you might also need to specify the path to your private key file using the `-i` flag.
bash
ssh -i ~/.ssh/my_private_key.pem -p 2345 [email protected]
Here, the client will use `my_private_key.pem` for authentication while connecting to `remote.host.com` on port `2345`.
Common Errors and Initial Troubleshooting
When first attempting to connect to a custom port, you might encounter issues. Here are some common problems and their potential causes:
- `ssh: connect to host [host] port [port_number]: Connection refused`:
- Cause: The most frequent error. This typically means that the SSH daemon (`sshd`) on the remote server is either not running, or it’s not listening on the specified port. It could also mean a firewall on the *server* is blocking the connection to that port.
- Solution: Verify that `sshd` is running on the server and is configured to listen on the correct custom port. Check the server’s firewall rules.
- `ssh: connect to host [host] port [port_number]: Operation timed out`:
- Cause: This usually indicates that a firewall *between* your client and the server is blocking the connection, or there’s a network routing issue preventing packets from reaching the server on that port.
- Solution: Review any intermediate firewalls (e.g., corporate firewall, router firewall) to ensure the custom port is allowed.
- `Permission denied (publickey,password).`:
- Cause: This means the connection to the port was successful, but your authentication failed. This is unrelated to the port itself.
- Solution: Double-check your username, password, or the SSH key you’re using. Ensure the public key is correctly installed on the server.
- Incorrect Port Number:
- Cause: A simple typo in the `port_number`.
- Solution: Carefully re-check the port number.
Using the verbose flag (`-v`, `-vv`, or `-vvv`) with your SSH command can provide invaluable debugging information, showing you the connection process step-by-step and helping pinpoint where the failure occurs.
bash
ssh -vvv -p 2222 [email protected]
Beyond the Command Line: Persistent Custom Port Configurations
While the `-p` flag is effective for one-off connections, repeatedly typing out custom ports can become tedious and error-prone. For frequent connections or managing multiple remote hosts, leveraging SSH configuration files provides a more elegant and efficient solution.
The SSH Client Configuration File (`~/.ssh/config`)
The SSH client configuration file, typically located at `~/.ssh/config` (in your home directory), allows you to define aliases and specific parameters for different remote hosts. This file is parsed by your SSH client *before* attempting a connection, enabling powerful customizations.
Why Use `~/.ssh/config`?
- Convenience: Define host aliases and eliminate the need to remember complex commands.
- Consistency: Ensure all connections to a specific host use the desired custom port and other parameters (e.g., username, identity file).
- Complexity Management: Simplify connections to hosts with intricate requirements (e.g., jump hosts, port forwarding).
- Automation: Easier scripting as you can refer to hosts by simple aliases.
Structure and Syntax
The `~/.ssh/config` file uses a simple, human-readable format. Each host entry begins with the `Host` directive, followed by an alias. Subsequent lines, indented, define specific parameters for that host.
Host [alias_name]
Hostname [remote_hostname_or_ip]
Port [custom_port_number]
User [remote_username]
IdentityFile [path_to_private_key]
# Add other options as needed
Example Configurations for Multiple Hosts with Custom Ports
Let’s set up configurations for a few hypothetical servers:
# Server for Development
Host dev-web
Hostname 192.168.1.10
Port 2222
User developer
IdentityFile ~/.ssh/id_rsa_dev
# Production Database Server
Host prod-db
Hostname prod-db.yourcompany.com
Port 54321
User dbadmin
IdentityFile ~/.ssh/id_rsa_prod
ForwardAgent yes # Example of another useful option
# A common alias for a public-facing server
Host bastion
Hostname 203.0.113.100
Port 22
User ubuntu
IdentityFile ~/.ssh/id_rsa_public
With these entries in your `~/.ssh/config` file, connecting becomes incredibly simple:
- To connect to `dev-web`: `ssh dev-web`
- To connect to `prod-db`: `ssh prod-db`
- To connect to `bastion`: `ssh bastion`
The SSH client automatically picks up the `Hostname`, `Port`, `User`, and `IdentityFile` values, making your command-line interactions much cleaner.
Wildcards and Advanced Options
The `~/.ssh/config` file also supports wildcards (`*` and `?`) for matching hosts and a wealth of other configuration directives. For instance:
# Apply these settings to all hosts
Host *
ServerAliveInterval 60
ServerAliveCountMax 3
# Apply these settings to hosts matching “stage-*”
Host stage-*
User staging_user
Port 2222
IdentityFile ~/.ssh/id_rsa_stage
This flexibility makes `~/.ssh/config` an indispensable tool for managing complex SSH environments, particularly when dealing with many servers using custom ports and specific authentication methods.
The SSH Server Configuration File (`/etc/ssh/sshd_config`)
While the client configuration tells *your machine* how to connect, the server configuration dictates *how the server listens* for connections. To truly use a custom port, you must configure the SSH daemon (`sshd`) on the remote server to listen on that port.
How to Change the Default Port on the Server Side
The server’s SSH configuration file is typically located at `/etc/ssh/sshd_config` (on Linux/Unix systems). You’ll need root privileges to edit this file.
1. Open the configuration file:
bash
sudo nano /etc/ssh/sshd_config
# Or use your preferred text editor like vi, vim, or gedit
2. Locate the `Port` directive:
By default, you’ll usually find a line like:
#Port 22
The `#` indicates that the line is commented out, meaning the default port 22 is implicitly used.
3. Change the port:
Uncomment the `Port` line (if commented) and change `22` to your desired custom port number. It’s generally a good practice to *add a new `Port` line* for your custom port and comment out or remove the default `Port 22` line *after* you’ve confirmed your custom port works. This ensures you still have an active SSH connection on 22 until you’re sure you can connect on the new port.
For example, to change it to port `2222`:
#Port 22 # Comment out or remove this line once you confirm custom port access
Port 2222 # Your new custom port
You can even specify multiple `Port` lines if you want `sshd` to listen on more than one port simultaneously.
4. Save changes and exit the editor.
Importance of Restarting `sshd`
For the changes in `/etc/ssh/sshd_config` to take effect, the SSH daemon service must be restarted. The exact command varies slightly depending on your Linux distribution:
- Systemd-based distributions (e.g., Ubuntu 16.04+, Debian 8+, CentOS 7+, Fedora):
bash
sudo systemctl restart sshd
- Note: On some older Ubuntu versions, the service might be named `ssh` instead of `sshd`. `sudo systemctl restart ssh`
- SysVinit-based distributions (older systems):
bash
sudo service ssh restart
Crucial Warning: Before restarting `sshd` or closing your current SSH session, ensure you have correctly configured your firewall to allow connections to the *new custom port*. Failure to do so could lock you out of your server. It’s often recommended to keep an existing SSH session open on port 22 while testing the new custom port from a *separate* terminal, so you can revert changes if something goes wrong.
Security Considerations for `sshd_config`
When modifying `/etc/ssh/sshd_config`, be mindful of other security directives:
- `PermitRootLogin no`: Disabling direct root login is a strong security practice.
- `PasswordAuthentication no`: Enforcing key-based authentication significantly enhances security.
- `AllowUsers`, `AllowGroups`, `DenyUsers`, `DenyGroups`: Restrict who can SSH into the server.
Always restart `sshd` cautiously and verify connectivity immediately after making changes.
Fortifying Your Defenses: Security Best Practices with Custom SSH Ports
Merely changing the SSH port is a foundational step, not a complete security strategy. A comprehensive approach integrates custom ports with other robust security measures.
1. Firewall Configuration: The Indispensable Guardian
The most critical step after changing the `sshd` port is to update your server’s firewall rules. If you change the port but don’t open it in the firewall, no one will be able to connect. Conversely, if you want to close off port 22 entirely, your firewall must enforce this.
Examples for Common Linux Firewalls:
- UFW (Uncomplicated Firewall – Ubuntu/Debian):
- Allow the new custom port (e.g., 2222):
bash
sudo ufw allow 2222/tcp
- (Optional) Disable default SSH port 22 access:
bash
sudo ufw deny 22/tcp
- Reload UFW:
bash
sudo ufw reload
- Firewalld (CentOS/RHEL/Fedora):
- Allow the new custom port (e.g., 2222):
bash
sudo firewall-cmd –permanent –add-port=2222/tcp
- (Optional) Remove default SSH service/port:
bash
sudo firewall-cmd –permanent –remove-service=ssh
# Or if you just want to remove the port explicitly:
# sudo firewall-cmd –permanent –remove-port=22/tcp
- Reload Firewalld:
bash
sudo firewall-cmd –reload
- Iptables (more granular, requires direct rule manipulation):
- Allow incoming connections on port 2222:
bash
sudo iptables -A INPUT -p tcp –dport 2222 -j ACCEPT
- (Optional) Drop incoming connections on port 22:
bash
sudo iptables -A INPUT -p tcp –dport 22 -j DROP
- Save iptables rules (varies by system, e.g., `sudo netfilter-persistent save` or `sudo service iptables save`).
Always test your new custom port connection *before* closing your existing SSH session on port 22 (if applicable). This provides a rollback path if you accidentally lock yourself out.
2. SSH Key-Based Authentication
Regardless of the port used, password authentication is inherently weaker than key-based authentication. Implement SSH keys for all your connections.
- Generate an SSH key pair on your local machine (`ssh-keygen`).
- Copy the public key to the remote server (`ssh-copy-id` or manual copy to `~/.ssh/authorized_keys`).
- Disable password authentication in `/etc/ssh/sshd_config` by setting `PasswordAuthentication no`.
3. Disable Root Login
Never permit direct root login via SSH. Instead, log in as a regular user and then use `sudo` to perform administrative tasks. Set `PermitRootLogin no` in `/etc/ssh/sshd_config`.
4. Implement Fail2Ban
Fail2Ban is an intrusion prevention software that scans log files (e.g., `/var/log/auth.log` or `/var/log/secure`) for repeated failed login attempts and dynamically blocks the offending IP addresses using firewall rules. Even with a custom port, brute-force attacks can occur, and Fail2Ban provides an automated defense.
- Configure Fail2Ban to monitor your SSH log files for your custom port. You’ll typically need to edit `/etc/fail2ban/jail.local` to specify the new port:
ini
[sshd]
enabled = true
port = 2222 # Your custom port
logpath = %(sshd_log)s
maxretry = 3
bantime = 1h
Remember to restart Fail2Ban after making changes.
5. Regular Audits and Software Updates
Keep your server’s operating system and all software packages, including SSH, up-to-date. Security vulnerabilities are frequently discovered and patched; applying updates promptly is crucial. Regularly audit your `sshd_config` file and firewall rules to ensure they align with your security posture.
Advanced Scenarios and Related Concepts
The utility of SSH with custom ports extends into more complex networking and security paradigms.
1. SSH Tunneling / Port Forwarding with Custom Ports
SSH’s power isn’t limited to remote shell access; it can also create secure tunnels to forward network traffic. Custom ports often play a role when the intermediary or destination server also uses a non-standard SSH port.
- Local Port Forwarding (`-L`): Access a service on a remote machine (or a machine reachable from it) through a local port.
bash
ssh -p 2222 -L 8080:internal-db.local:5432 [email protected]
Here, the SSH connection to `bastion-host.com` uses port `2222`. Once connected, traffic to your local `localhost:8080` will be forwarded through the secure tunnel to `internal-db.local:5432`.
- Remote Port Forwarding (`-R`): Make a local service available to others through a remote port on the SSH server.
bash
ssh -p 2222 -R 8000:localhost:3000 [email protected]
This connects to `remote-host.com` on port `2222` and exposes your local machine’s service on port `3000` to port `8000` on `remote-host.com`.
2. Using SSH with Proxies and Jump Hosts
In enterprise environments, direct SSH connections to internal servers are often prohibited. Instead, you connect to a “jump host” or “bastion host” that then acts as a relay to internal machines. Custom ports can be used on both the jump host and the final target.
The `ProxyCommand` directive in `~/.ssh/config` is invaluable here:
Host internal-server
Hostname 10.0.0.50
User internal_user
Port 22 # The port on the internal server
ProxyCommand ssh -p 2222 -W %h:%p [email protected]
IdentityFile ~/.ssh/id_rsa_internal
Now, when you run `ssh internal-server`, your client first connects to `bastion.example.com` on its custom port `2222`. Through that connection, it then establishes a tunnel to `internal-server`’s standard port 22, making the connection seamless from your perspective.
3. Scripting SSH Connections
Automating tasks that involve SSH with custom ports is common. You can embed the `-p` flag directly into scripts or, more elegantly, rely on `~/.ssh/config` aliases.
Using `-p` directly in scripts:
bash
#!/bin/bash
SSH_USER=”automation”
SSH_HOST=”monitoring-server.example.com”
SSH_PORT=”2222″
COMMAND=”df -h /var/log”
ssh -p “${SSH_PORT}” “${SSH_USER}@${SSH_HOST}” “${COMMAND}”
Using `~/.ssh/config` alias (preferred):
bash
#!/bin/bash
SSH_ALIAS=”monitoring-server” # Alias defined in ~/.ssh/config
COMMAND=”df -h /var/log”
ssh “${SSH_ALIAS}” “${COMMAND}”
This approach makes scripts more readable and easier to maintain, as all connection details are centralized in the config file.
Troubleshooting Common Issues with Custom Ports
Even with careful configuration, issues can arise. Knowing how to diagnose them efficiently is key.
- “Connection refused”:
- Verify `sshd` status on server: Is the SSH daemon running? `sudo systemctl status sshd`
- Check `sshd_config`: Is the `Port` directive correctly set to the custom port? Did you restart `sshd`?
- Firewall on server: Is the custom port open in the server’s firewall (`ufw`, `firewalld`, `iptables`)?
- “Operation timed out”:
- Intermediate firewalls: Are there any firewalls between your client and the server (e.g., corporate network firewall, cloud security groups) blocking the custom port?
- Network connectivity: Can your client reach the server at all? Try `ping` (though ICMP might also be blocked).
- Incorrect `ssh` client syntax:
- Did you use `-p` (lowercase) for the port number? Using `-P` (uppercase) is a common mistake.
- Is the port number valid (1-65535)? Well-known ports are 0-1023, registered ports are 1024-49151, and dynamic/private ports are 49152-65535.
- `ssh -v` for verbose output:
- When troubleshooting, always add one or more `-v` flags (`-v`, `-vv`, `-vvv`) to your SSH command. This will provide detailed debugging output, showing each step of the connection process and often pinpointing the exact failure point.
- Example: `ssh -vvv -p 2222 user@host`
Conclusion
Mastering the SSH command with a custom port is a fundamental skill that transcends basic remote access. It’s a strategic choice that contributes significantly to the security, resilience, and manageability of your digital infrastructure. While it doesn’t represent a silver bullet for all security concerns, moving SSH to a non-standard port acts as an effective initial filter, reducing exposure to pervasive automated attacks and allowing your team to focus on more sophisticated threats.
Beyond security, the judicious use of custom ports, especially when integrated with client-side configuration files like `~/.ssh/config`, dramatically enhances operational efficiency. It simplifies complex connections, streamlines scripting, and fosters a more organized approach to managing diverse server environments.
By understanding the `ssh -p` flag, configuring both client and server-side settings, and diligently applying best practices for firewalls, key-based authentication, and intrusion detection, you transform a simple command into a powerful instrument for secure and flexible remote administration. The digital frontier is constantly evolving, and your command of SSH, including its custom port capabilities, ensures you remain a step ahead in securing and managing your critical systems.