In an increasingly interconnected digital landscape, the concept of privacy has evolved from a mere preference to an absolute necessity. Every click, every search, every online interaction leaves a digital footprint, with your Internet Protocol (IP) address serving as the most prominent identifier. For individuals, businesses, and even governments, understanding and controlling this digital presence is paramount. While various tools promise online anonymity, few offer the granular control, security, and underlying technical elegance of an SSH tunnel. This comprehensive guide delves deep into the mechanics, benefits, and practical applications of leveraging Secure Shell (SSH) tunnels to effectively mask your IP address, offering a robust alternative for those who demand more from their privacy solutions.
Our journey into the realm of IP address concealment will not merely skim the surface. We will dissect the fundamental principles, walk through detailed implementation steps for various operating systems, and explore advanced considerations that elevate SSH tunneling from a mere trick to a sophisticated cybersecurity strategy. Whether you’re a seasoned network administrator, a privacy advocate, or simply someone looking to reclaim their digital autonomy, this article provides the insights and actionable knowledge required to master this powerful technique.
Understanding the Digital Fingerprint: What Exactly is an IP Address?
Before we embark on the mission of hiding your IP address, it’s crucial to grasp what it truly represents. An IP address is a unique numerical label assigned to every device connected to a computer network that uses the Internet Protocol for communication. Think of it as your device’s postal address on the internet. Just as a physical address directs mail to your home, an IP address directs data packets to your specific device.
There are two primary versions of IP addresses in use today: IPv4 and IPv6. IPv4 addresses, like 192.168.1.1, are more common but are rapidly depleting. IPv6 addresses, such as 2001:0db8:85a3:0000:0000:8a2e:0370:7334, are designed to accommodate the exponential growth of internet-connected devices. Your Internet Service Provider (ISP) assigns you a public IP address, which is visible to the websites and online services you interact with. This public IP reveals your approximate geographical location, your ISP, and can often be linked back to your account, forming a critical component of your digital identity.
The Imperative of IP Hiding: Why Online Anonymity Matters
The reasons for wanting to hide your IP address are manifold and extend far beyond illicit activities, a common misconception. For many, it’s about reclaiming a fundamental right to privacy in an era of pervasive surveillance and data exploitation. Here are some compelling reasons why IP masking has become an imperative:
- Enhanced Privacy and Anonymity: Prevent websites, advertisers, and data brokers from tracking your online activities, building comprehensive profiles, and selling your browsing habits.
- Bypassing Geo-Restrictions: Access content or services that are geographically restricted. This is particularly useful for streaming services, news outlets, or online games available only in specific regions.
- Securing Public Wi-Fi Connections: Public Wi-Fi networks are notorious for their lack of security. Hiding your IP address and encrypting your traffic adds a crucial layer of protection against eavesdropping and man-in-the-middle attacks.
- Evading Censorship: In regions with strict internet censorship, masking your IP can help bypass government firewalls and access blocked information.
- Protecting Against Targeted Attacks: Obscuring your actual IP makes it harder for malicious actors to target your specific location or network with denial-of-service (DoS) attacks or other cyber threats.
- Maintaining Business Confidentiality: For businesses, hiding the IP can protect proprietary information, competitive intelligence, and ensure secure communication channels for remote workers.
- Preventing Price Discrimination: Some e-commerce sites use IP addresses to determine your location and adjust pricing, a practice that can be circumvented by masking your IP.
The ability to control your IP address is, therefore, a cornerstone of modern digital literacy and cybersecurity hygiene.
Introducing SSH: More Than Just Remote Access
Secure Shell (SSH) is a cryptographic network protocol that enables secure remote login and other secure network services over an unsecured network. Developed as a secure replacement for Telnet and other insecure remote shells, SSH provides strong authentication and encrypted communication between two networked devices. Its primary use case involves securely accessing remote servers and executing commands.
However, the true power of SSH extends far beyond simple remote access. Built into its architecture is a robust tunneling mechanism, allowing it to forward arbitrary network ports over an encrypted connection. This capability is what transforms SSH from a mere administrative tool into a formidable privacy-enhancing technology. When you establish an SSH connection, all data traveling through that connection is encrypted, making it unreadable to anyone intercepting the traffic between your client and the SSH server. This inherent security is precisely why SSH tunnels are so effective for hiding your IP address and safeguarding your online communications.
The Power of SSH Tunnels: A Deep Dive into Secure Port Forwarding
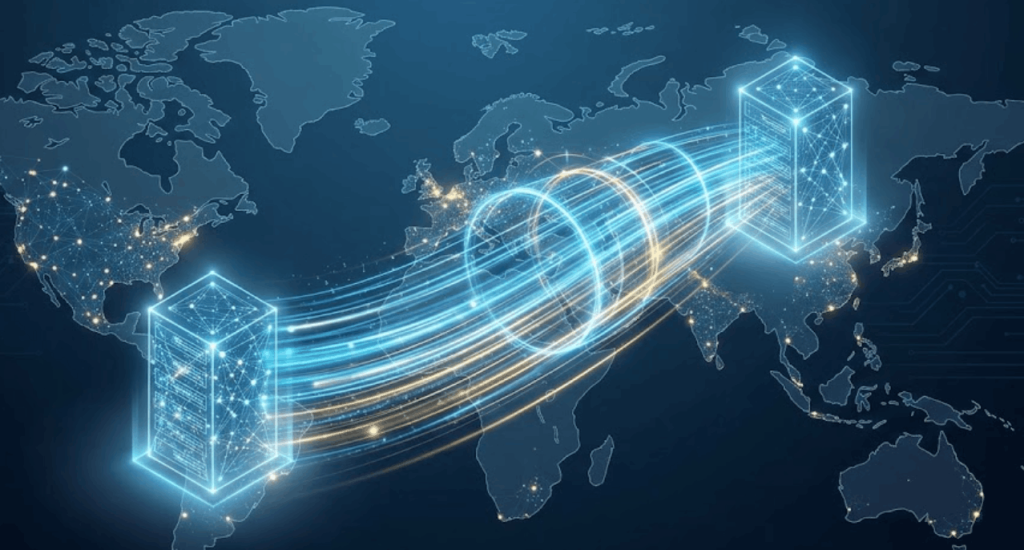
At its core, an SSH tunnel creates an encrypted pathway through an SSH connection. Imagine you want to send a sensitive letter from your home (your computer) to a friend (a website). Normally, this letter travels through a public postal service (your ISP), where anyone could potentially read the envelope (your IP address) or even its contents if unsealed. An SSH tunnel is like sending that letter inside a locked, armored car directly to a trusted post office (your SSH server) in another city. From that post office, the letter is then sent to your friend. Your friend only sees the address of the trusted post office, not your home address.
This “armored car” analogy perfectly illustrates how SSH tunneling works. Your network traffic, instead of going directly from your device to its destination, is first encapsulated and encrypted within the SSH connection. It travels securely to a remote SSH server. From that server, the traffic is then decrypted and sent to its final destination on the internet. The recipient of your traffic (e.g., a website) will see the IP address of your SSH server, not your actual IP address.
There are three main types of SSH port forwarding:
- Local Port Forwarding: Connects a local port on your machine to a port on the remote server, which then forwards to a destination server. Useful for accessing internal services.
- Remote Port Forwarding: Connects a port on the remote server to a port on your local machine, allowing others to access a local service through the remote server.
- Dynamic Port Forwarding: This is our focus. It creates a SOCKS proxy on your local machine. All applications configured to use this SOCKS proxy will send their traffic through the encrypted SSH tunnel to the remote SSH server, and from there, to the internet. This is the most versatile method for IP masking, as it can handle multiple types of network traffic.
Dynamic Port Forwarding: Your Gateway to True IP Anonymity
Dynamic port forwarding, often referred to as a SOCKS proxy over SSH, is the most powerful and flexible method for hiding your IP address using SSH. It essentially turns your SSH server into a proxy server for your internet traffic. When you configure your browser or other applications to use this SOCKS proxy, all their outgoing connections are rerouted through the encrypted SSH tunnel to your remote server, making your server’s IP address appear as your own to the outside world.
Prerequisites for Setting Up an SSH Tunnel
Before diving into the configuration steps, ensure you have the following:
- An SSH Client: Most Linux and macOS systems come with OpenSSH pre-installed. For Windows, PuTTY is the most popular and robust option.
- An SSH Server: You need access to a remote server with an SSH daemon running. This could be a Virtual Private Server (VPS) you rent from a provider like DigitalOcean, Vultr, AWS, or Linode, or even a personal server you control at a different location. Crucially, you must trust the owner/provider of this SSH server, as all your traffic will pass through it.
- SSH Credentials: A username and password, or preferably, an SSH key pair (public/private key) for authentication on the remote server. Key-based authentication is significantly more secure.
Step-by-Step Guide: Linux/macOS (OpenSSH)
Setting up a dynamic SSH tunnel on Unix-like systems is straightforward using the terminal.
- Open Your Terminal: Access your command-line interface.
- Execute the SSH Command: Use the following command syntax:
ssh -D 8080 -N -f your_username@your_ssh_server_ip_or_hostname-D 8080: This is the core of dynamic port forwarding. It tells SSH to create a SOCKS proxy on your local machine, listening on port8080. You can choose any unused port number (e.g., 1080, 9000).-N: This flag prevents SSH from executing a remote command. We only want to forward ports, not open a shell.-f: This tells SSH to go into the background immediately after authentication. This allows you to continue using your terminal while the tunnel runs in the background.your_username@your_ssh_server_ip_or_hostname: Replaceyour_usernamewith your actual username on the remote SSH server andyour_ssh_server_ip_or_hostnamewith the IP address or hostname of your SSH server.
Example:
ssh -D 8080 -N -f [email protected]If you’re using SSH keys for authentication, ensure your private key is loaded (e.g., via
ssh-agent) or specify it with-i /path/to/your/private_key. - Enter Your Password (if applicable): If you’re not using SSH keys, you’ll be prompted for your remote server’s password.
- Verify the Tunnel (Optional): You can check if the tunnel is listening on the specified port using
netstat -tulnp | grep 8080(on Linux) orlsof -i :8080(on macOS). You should see a process listening on127.0.0.1:8080. - Configure Your Applications to Use the SOCKS Proxy:
- Firefox: Go to
Settings->Network Settings->Settings.... SelectManual proxy configuration. ForSOCKS Host, enter127.0.0.1and forPort, enter8080(or whatever port you chose). SelectSOCKS v5. Ensure “Proxy DNS when using SOCKS v5” is checked for full anonymity. - Google Chrome/Chromium: Chrome typically uses your system’s proxy settings. On macOS, go to
System Settings->Network->(Your Active Network)->Details...->Proxies. EnableSOCKS Proxy, enter127.0.0.1and port8080. On Linux, this often involves modifying environment variables or using a proxy management tool. Alternatively, you can use browser extensions like “Proxy SwitchyOmega” for more granular control within Chrome. - Other Applications: Most applications that support proxy settings will have an option to configure a SOCKS v5 proxy.
- Firefox: Go to
Step-by-Step Guide: Windows (PuTTY)
PuTTY is the go-to SSH client for Windows users and provides a graphical interface for setting up tunnels.
- Download and Install PuTTY: If you don’t have it, download PuTTY from its official website.
- Launch PuTTY: Open the PuTTY application.
- Configure Your SSH Connection:
- In the
Sessioncategory, enter your SSH server’sHostname (or IP address)(e.g.,your_ssh_server_ip_or_hostname). ThePortshould typically be22(the default SSH port). - Give your session a name in
Saved Sessionsand clickSave.
- In the
- Configure Dynamic Port Forwarding:
- Navigate to
Connection->SSH->Tunnelsin the left-hand category tree. - Under
Add new forwarded port:, forSource port, enter8080(or your chosen local port). - Select the
Dynamicradio button. - Click the
Addbutton. You should seeD8080appear in theForwarded portslist.
- Navigate to
- Save Your Configuration: Go back to the
Sessioncategory, select your saved session, and clickSaveagain to preserve your tunnel settings. - Open the SSH Connection: Click
Open. You’ll be prompted for your username and password for the remote server. If using SSH keys, configure them underConnection->SSH->Auth->Credentialsby browsing for your private key file (.ppkformat for PuTTY). After successful authentication, a terminal window will open, but you don’t need to do anything in it; just keep it open to maintain the tunnel. - Configure Your Applications to Use the SOCKS Proxy: (Same as Linux/macOS steps for browsers and other applications). For Windows system-wide proxy settings: Go to
Settings->Network & Internet->Proxy. UnderManual proxy setup, toggleUse a proxy servertoOn. ForSOCKS, enter127.0.0.1and port8080.
Verification: Confirming Your IP Address is Hidden
Once your tunnel is active and your applications are configured to use the SOCKS proxy, open your configured browser and navigate to a “What’s My IP” website (e.g., whatismyip.com, ipinfo.io). The IP address displayed should be that of your remote SSH server, not your actual public IP address. This confirms your IP is successfully masked.
Beyond Basic Anonymity: Advanced Considerations and Best Practices
While setting up a basic SSH tunnel is relatively simple, achieving robust and reliable IP anonymity requires attention to several advanced considerations.
Choosing Your SSH Server Wisely
The security and effectiveness of your SSH tunnel are directly tied to the SSH server you use. Consider the following:
- Trustworthiness: Only use an SSH server from a provider or entity you implicitly trust. All your traffic passes through this server, meaning the server administrator could potentially monitor your activities if they choose to. Avoid free, public SSH servers unless you fully understand and accept the risks.
- Location: The physical location of your SSH server dictates the IP address that external services will see. Choose a server location that aligns with your anonymity goals (e.g., bypassing geo-restrictions for a specific country). Proximity also affects latency.
- Logging Policies: Research the logging policies of your VPS provider. Some providers maintain extensive logs, which could compromise your anonymity if subpoenaed. Opt for providers known for their privacy-friendly policies.
- Server Security: Ensure your SSH server is well-maintained, patched regularly, and configured with strong security practices (e.g., disable password authentication, use SSH keys, fail2ban).
Security Implications and Best Practices
Even with an SSH tunnel, security is paramount:
- SSH Key Authentication: Always prefer SSH key pairs over passwords. Generate strong, unique keys and protect your private key with a strong passphrase.
- Strong Passwords: If you must use passwords, ensure they are complex, unique, and long.
- Regular Updates: Keep your SSH client (OpenSSH, PuTTY) and your SSH server’s operating system and SSH daemon updated to protect against known vulnerabilities.
- Firewall Configuration: Configure your local firewall to only allow outbound SSH connections to your trusted server and incoming connections only for the SOCKS proxy port (if needed for other local applications).
Performance Considerations
Routing your traffic through an SSH tunnel introduces an additional hop and encryption overhead, which can impact performance:
- Latency: The geographical distance between you and your SSH server significantly affects latency (ping time). Choose a server geographically closer to you for better responsiveness, unless your goal is to appear in a specific distant location.
- Bandwidth: Your internet speed will be limited by the lowest bandwidth between your client, the SSH server, and the final destination. Ensure your VPS has adequate bandwidth.
- CPU Usage: Encryption and decryption require CPU cycles on both your client and the server. For heavy traffic, ensure your server has sufficient processing power.
When to Use SSH Tunnels vs. VPNs
SSH tunnels and Virtual Private Networks (VPNs) both aim to enhance privacy and security, but they operate differently and cater to distinct use cases.
SSH Tunnel Advantages:
- Granular Control: You control the server, the encryption, and the specific applications using the tunnel.
- Cost-Effective: If you already own a VPS, it’s virtually free. Renting a basic VPS is often cheaper than a premium VPN service.
- Lightweight: Less overhead than a full VPN client, often ideal for specific tasks or single applications.
- Bypassing Restrictive Firewalls: Can sometimes penetrate firewalls that block standard VPN protocols because it uses the common SSH port (22).
SSH Tunnel Disadvantages:
- Complexity: Requires some technical know-how to set up and manage.
- Application-Specific: By default, it only proxies traffic for applications explicitly configured to use the SOCKS proxy. System-wide tunneling is more complex.
- Single Server: You’re typically tied to one SSH server, unlike VPNs that offer a network of servers.
- No Kill Switch: If the tunnel drops, your real IP is exposed, unless you’ve implemented additional measures.
VPN Advantages:
- Ease of Use: User-friendly apps for all major platforms, often one-click connect.
- System-Wide Protection: Encrypts all network traffic from your device by default.
- Advanced Features: Kill switches, DNS leak protection, ad blocking, split tunneling, and a large network of servers.
- Dedicated Support: Commercial VPN providers offer customer support.
VPN Disadvantages:
- Cost: Typically a recurring subscription fee.
- Trust: You must trust the VPN provider’s logging policies and security practices.
- Less Control: You have less direct control over the server and encryption parameters.
Conclusion: Use an SSH tunnel for specific applications, when you need fine-grained control, or when standard VPNs are blocked. Opt for a VPN for general, system-wide protection and ease of use, especially if you’re not technically inclined.
Practical Applications and Use Cases for SSH Tunnels
The utility of SSH tunnels extends across numerous scenarios, providing robust solutions for various digital challenges:
- Bypassing Geo-Restrictions: As discussed, this is a primary use. Access region-locked content from streaming services, news sites, or online stores by connecting to an SSH server located in the desired country.
- Securing Public Wi-Fi Connections: When connected to unsecured public Wi-Fi at a cafe, airport, or hotel, an SSH tunnel encrypts your traffic from your device to your trusted server, protecting you from malicious actors on the local network.
- Accessing Internal Network Resources Remotely: Developers or system administrators can use local port forwarding (a variation of SSH tunneling) to securely access internal services (like a database, web server, or development environment) on a remote network as if they were local, without exposing those services directly to the internet.
- Enhancing Development Workflows: Developers can use SSH tunnels to securely connect to remote Git repositories, Docker daemons, or other development tools without relying on less secure methods.
- Circumventing ISP Throttling: Some ISPs might throttle specific types of traffic (e.g., torrents, streaming). Encrypting and tunneling this traffic can sometimes obscure its nature from the ISP, potentially bypassing throttling.
- Testing Geo-Specific Features: Web developers can test how their websites or applications behave for users in different geographical locations by tunneling their traffic through servers in those regions.
Maintaining Your Digital Shield: Tips for Ongoing Privacy
Establishing an SSH tunnel is a significant step towards enhancing your online privacy, but it’s not a set-it-and-forget-it solution. Ongoing vigilance and best practices are essential:
- Regularly Monitor Your IP Address: Periodically check your IP address using “What’s My IP” services to ensure your tunnel is still active and functioning correctly.
- Manage SSH Keys Securely: Keep your private SSH keys secure, ideally encrypted with a strong passphrase, and never share them. Rotate them periodically.
- Keep Your Server Updated: Ensure your remote SSH server’s operating system and SSH daemon are always up-to-date with the latest security patches.
- Consider DNS Leaks: While dynamic port forwarding with SOCKS v5 typically proxies DNS requests, it’s wise to perform a DNS leak test (e.g.,
dnsleaktest.com) to ensure your actual DNS servers aren’t being revealed. - Combine with Other Privacy Tools: For ultimate anonymity, consider layering your SSH tunnel with other privacy tools, such as Tor Browser, though this can significantly impact performance.
Conclusion: Reclaiming Your Digital Autonomy
In a digital world where personal data is the new currency, the ability to control and mask your IP address is a powerful tool for safeguarding your privacy and security. SSH tunnels, with their robust encryption and flexible port forwarding capabilities, offer a technically elegant and highly effective method for achieving this. While they may require a slightly steeper learning curve than commercial VPNs, the unparalleled control and transparency they provide are invaluable for those who prioritize digital autonomy.
By understanding the mechanics of dynamic port forwarding, implementing best practices for server selection and security, and remaining vigilant about your online footprint, you can effectively hide your IP address and navigate the internet with a renewed sense of privacy. Embrace the power of SSH tunnels, and reclaim your rightful place as the master of your digital identity.
Frequently Asked Questions (Q&A) About Hiding Your IP Address with SSH Tunnels
Q1: Is an SSH tunnel as secure as a VPN?
A1: Both SSH tunnels and VPNs offer strong encryption for your data in transit. The “security” largely depends on the implementation and trustworthiness of the server. An SSH tunnel, when configured correctly with strong authentication (like SSH keys) and a trusted server you control, can be extremely secure for the specific traffic it handles. VPNs, especially commercial ones, often offer additional features like a kill switch, DNS leak protection, and a wider network of servers, making them more comprehensive for system-wide protection. For specific application traffic, an SSH tunnel can be just as secure, if not more, due to the direct control you have over the server.
Q2: Can my ISP see that I’m using an SSH tunnel?
A2: Your ISP can see that you are making an SSH connection to a remote server (typically on port 22). However, they cannot see the content of that connection because it is encrypted. They also cannot see what kind of traffic is being tunneled inside the SSH connection (e.g., web browsing, email). They will only see encrypted SSH packets flowing between your device and your SSH server. From the ISP’s perspective, it looks like you’re just securely accessing a remote machine.
Q3: What are the risks of using a free or public SSH server?
A3: The primary risk is a lack of trust. When you tunnel your traffic through an SSH server, the server administrator can potentially see all the unencrypted traffic once it exits the tunnel on their side. Free or public SSH servers are often run by unknown entities with unknown logging policies. They could log your activities, inject malware, or even sell your data. It’s strongly recommended to use an SSH server you own or rent from a reputable VPS provider with clear privacy policies.