Mastering SSH: An Indispensable Tutorial for Your Ubuntu Server
In the realm of server administration, the ability to securely and efficiently manage remote systems is not merely a convenience; it is an absolute necessity. For anyone operating an Ubuntu server, Secure Shell (SSH) stands as the bedrock of this capability, offering a cryptographic network protocol for operating network services securely over an unsecured network. From deploying applications to routine maintenance, understanding and mastering SSH is paramount.
This deeply comprehensive guide aims to demystify SSH for Ubuntu server users, transforming novices into confident administrators capable of leveraging its full potential. We will navigate through its foundational principles, practical implementation, and advanced security considerations, ensuring your remote server interactions are both robust and secure.
The Cornerstone of Remote Server Management: What is SSH?
At its core, SSH is a network protocol that allows data to be exchanged using a secure channel between two networked devices. Introduced in 1995 as a secure replacement for Telnet, rlogin, and rsh, which transmitted data in plaintext, SSH encrypts all traffic to prevent eavesdropping, connection hijacking, and other attacks. This encryption is crucial when managing servers over potentially insecure networks like the internet.
For Ubuntu server users, SSH provides a text-based interface (a shell) to interact with the server as if you were sitting directly in front of it. This remote command-line access is the primary method for installing software, configuring services, managing files, and performing virtually any administrative task. Beyond shell access, SSH also facilitates secure file transfers (SCP, SFTP) and even tunneling of arbitrary network ports.
Prerequisites for Your SSH Journey
Before embarking on the practical steps, ensure you have the following in place:
- An Ubuntu Server: This tutorial assumes you have a running Ubuntu server instance (e.g., Ubuntu Server 20.04 LTS or 22.04 LTS). This could be a virtual machine, a dedicated server, or a cloud instance.
- Internet Connection: Both your local machine (client) and the Ubuntu server need internet connectivity.
- Basic Command-Line Familiarity: While this guide will be explicit, a rudimentary understanding of Linux command-line operations will be beneficial.
- Server IP Address or Hostname: You’ll need the public IP address or a resolvable hostname of your Ubuntu server.
- User Credentials: You should have the username and password for a user account on your Ubuntu server, preferably one with `sudo` privileges.
Setting Up SSH on Your Ubuntu Server (Server-Side Configuration)
The first step to establishing a secure remote connection is to ensure your Ubuntu server is configured to accept SSH connections. Most Ubuntu server installations come with the OpenSSH server pre-installed, but it’s good practice to verify and understand its setup.
Verifying OpenSSH Server Installation
To check if the OpenSSH server is already installed on your Ubuntu server, execute the following command:
bash
sudo systemctl status ssh
If it’s running, you’ll see output indicating `active (running)`. If it’s not installed or not running, the output will differ.
Installing OpenSSH Server
If the OpenSSH server (often referred to as `sshd`) is not installed, you can easily install it using the Advanced Package Tool (APT):
1. Update Package Lists:
It’s always a good idea to update your local package index before installing new software.
bash
sudo apt update
2. Install OpenSSH Server:
bash
sudo apt install openssh-server
Confirm the installation when prompted. Once installed, the `ssh` service should start automatically.
3. Verify Service Status (Again):
bash
sudo systemctl status ssh
You should now see it as `active (running)`.
Configuring the Firewall (UFW)
Ubuntu servers typically use UFW (Uncomplicated Firewall) to manage network access. It’s crucial to allow SSH connections through the firewall, otherwise, you won’t be able to connect remotely.
1. Check UFW Status:
bash
sudo ufw status
If UFW is inactive, you can skip to step 3 for now, but it’s highly recommended to enable it later for security. If it’s active, proceed to step 2.
2. Allow SSH Traffic:
UFW has a predefined profile for SSH, making it simple to allow access.
bash
sudo ufw allow ssh
This command typically allows traffic on port 22 (the default SSH port). If you plan to change the default SSH port, you would allow that specific port number instead (e.g., `sudo ufw allow 2222/tcp`).
3. Enable UFW (if inactive):
If UFW was inactive, enable it now. Be careful: ensure you’ve allowed SSH *before* enabling UFW, otherwise you might lock yourself out.
bash
sudo ufw enable
Confirm the action when prompted.
4. Verify UFW Rules:
bash
sudo ufw status verbose
You should see an entry indicating that SSH (or port 22) is allowed.
Basic `sshd_config` File Configuration
The primary configuration file for the OpenSSH server is `/etc/ssh/sshd_config`. Modifying this file allows you to customize various aspects of SSH behavior, enhancing security and functionality. Always back up the original file before making changes:
bash
sudo cp /etc/ssh/sshd_config /etc/ssh/sshd_config.bak
Now, open the file for editing:
bash
sudo nano /etc/ssh/sshd_config
Here are some crucial settings you might want to adjust (we’ll dive deeper into security later):
- `Port 22`: This defines the port `sshd` listens on. While 22 is the default, changing it to a non-standard port (e.g., `Port 2222`) can deter automated scanning bots, though it’s not a strong security measure against targeted attacks. Remember to update your UFW rules if you change this.
- `PermitRootLogin yes`: By default, this is often set to `prohibit-password` or `no`. It’s highly recommended to disable direct root login for security reasons. Change this to `PermitRootLogin no`. You can always log in as a regular user and then use `sudo` to gain root privileges.
- `PasswordAuthentication yes`: This allows users to log in with a password. While convenient for initial setup, it’s significantly less secure than SSH key authentication. For stronger security, especially after setting up SSH keys, consider changing this to `PasswordAuthentication no`.
- `X11Forwarding yes`: Allows for graphical applications to be run remotely, with their display forwarded to your local machine. Keep this `no` if you don’t need it.
After making any changes to `sshd_config`, you must restart the SSH service for them to take effect:
bash
sudo systemctl restart ssh
Connecting to Your Ubuntu Server via SSH (Client-Side)
With the server configured, you’re ready to initiate a connection from your local machine. The process varies slightly depending on your operating system.
From Linux or macOS
Both Linux and macOS come with an SSH client pre-installed, making connections straightforward.
1. Open Terminal: Launch your terminal application.
2. Connect: Use the `ssh` command followed by your username on the server and its IP address or hostname.
bash
ssh username@your_server_ip_or_hostname
Replace `username` with your actual username on the Ubuntu server (e.g., `sammy`) and `your_server_ip_or_hostname` with the server’s IP address (e.g., `192.168.1.100`) or its domain name (e.g., `example.com`).
Example:
bash
ssh [email protected]
If you changed the default SSH port, you’ll need to specify it using the `-p` flag:
bash
ssh -p 2222 [email protected]
3. First Connection Fingerprint: The very first time you connect to a new server, SSH will ask you to verify the server’s host key fingerprint. This is a crucial security measure to prevent “man-in-the-middle” attacks.
The authenticity of host ‘192.168.1.100 (192.168.1.100)’ can’t be established.
ECDSA key fingerprint is SHA256:abcd…
Are you sure you want to continue connecting (yes/no/[fingerprint])?
You should type `yes` and press Enter. The server’s fingerprint will be saved to your `~/.ssh/known_hosts` file, so you won’t be prompted again unless the server’s key changes (which could indicate a security issue).
4. Enter Password: After confirming the fingerprint, you’ll be prompted for your user’s password on the Ubuntu server. Type it carefully (characters won’t appear on screen for security) and press Enter.
[email protected]’s password:
Upon successful authentication, you will be granted access to the server’s command-line interface.
From Windows
Connecting from Windows typically involves either the built-in OpenSSH client (available in Windows 10/11) or a third-party client like PuTTY.
##### Using the Built-in OpenSSH Client (Windows 10/11)
Windows 10 and 11 include a native OpenSSH client accessible via PowerShell or Command Prompt, mirroring the Linux/macOS experience.
1. Open PowerShell or Command Prompt: Search for “PowerShell” or “CMD” in the Start menu.
2. Connect: The command is identical to Linux/macOS:
bash
ssh username@your_server_ip_or_hostname
Remember to use `-p` if you changed the port.
3. Follow On-Screen Prompts: You’ll encounter the same fingerprint verification and password prompt as described for Linux/macOS.
##### Using PuTTY (Older Windows Versions or Preference)
PuTTY is a popular free and open-source SSH client for Windows.
1. Download PuTTY: Visit the official PuTTY download page (`www.putty.org`) and download the appropriate `.msi` installer or `putty.exe` executable.
2. Launch PuTTY: Open the PuTTY application.
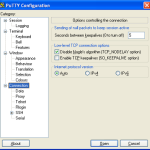
3. Configure Session:
- In the “Host Name (or IP address)” field, enter your server’s IP address or hostname.
- Ensure the “Port” is set to 22 (or your custom SSH port).
- Ensure “Connection type” is set to SSH.
- You can optionally enter a “Saved Sessions” name and click “Save” to quickly reconnect later.
4. Open Connection: Click the “Open” button.
5. Security Alert: If it’s your first connection, PuTTY will show a “PuTTY Security Alert” asking you to verify the server’s host key. Click “Accept” (after verifying the fingerprint if possible) to cache the key and proceed.
6. Login: A terminal window will open, prompting you for your `login as:` username, then your password. Enter them to gain access.
Fundamental SSH Operations
Once connected, you have a powerful conduit to your server. Here are some basic, yet essential, operations.
Executing Commands Remotely
Any command you type in the SSH terminal is executed on the remote Ubuntu server.
- Check system uptime:
bash
uptime
- List files in your home directory:
bash
ls -l
- Update server packages:
bash
sudo apt update && sudo apt upgrade
You’ll be prompted for your password again for `sudo` commands.
Transferring Files with SCP and SFTP
SSH isn’t just for shell access; it also provides secure mechanisms for file transfer.
##### SCP (Secure Copy Protocol)
SCP is a command-line utility for copying files and directories between machines over an SSH connection.
- Copy a local file to the remote server:
bash
scp /path/to/local/file.txt username@your_server_ip:/path/to/remote/directory/
Example: `scp my_script.sh [email protected]:/home/sammy/scripts/`
- Copy a file from the remote server to your local machine:
bash
scp username@your_server_ip:/path/to/remote/file.txt /path/to/local/directory/
Example: `scp [email protected]:/var/log/syslog ~/server_logs/`
- Copy a directory recursively: Use the `-r` option for directories.
bash
scp -r /path/to/local/directory/ username@your_server_ip:/path/to/remote/directory/
Example: `scp -r my_app_folder [email protected]:/var/www/`
- Specify a non-standard port: Use the `-P` (uppercase) option.
bash
scp -P 2222 localfile.txt [email protected]:/home/sammy/
##### SFTP (SSH File Transfer Protocol)
SFTP provides an interactive command-line interface for file transfer, similar to FTP but secure. It’s often preferred for more complex file management tasks, such as navigating directories, creating new ones, or resuming transfers.
1. Initiate an SFTP session:
bash
sftp username@your_server_ip
(Add `-P 2222` for a custom port).
2. Common SFTP Commands:
- `ls`: List files on the remote server.
- `lls`: List files on your local machine.
- `cd /remote/path`: Change directory on the remote server.
- `lcd /local/path`: Change directory on your local machine.
- `get remote_file.txt`: Download a file from the server.
- `put local_file.txt`: Upload a file to the server.
- `mget *.log`: Download multiple files matching a pattern.
- `mput *.conf`: Upload multiple files matching a pattern.
- `exit` or `bye`: Exit the SFTP session.
Elevating Security: Best Practices for SSH on Ubuntu Server
While SSH is inherently secure, misconfigurations can create vulnerabilities. Implementing these best practices is vital for hardening your server.
1. SSH Key Authentication: The Gold Standard
Password authentication is susceptible to brute-force attacks and weak passwords. SSH keys provide a much stronger, cryptographically secure alternative.
How it Works: You generate a pair of keys: a private key (kept secret on your local machine) and a public key (uploaded to your server). When you connect, your client proves ownership of the private key, and the server verifies it against the public key. No passwords are exchanged.
##### Generating SSH Keys (on your local machine)
1. Open Terminal/PowerShell:
bash
ssh-keygen -t rsa -b 4096
- `-t rsa`: Specifies the RSA algorithm (you can also use `ed25519` for a more modern option).
- `-b 4096`: Specifies a 4096-bit key length, which is very strong.
2. Save Location: The command will prompt you where to save the keys (default is `~/.ssh/id_rsa`). Press Enter to accept the default.
3. Passphrase: You’ll be asked for a passphrase. This is highly recommended. It encrypts your private key, so even if someone gets hold of it, they can’t use it without the passphrase. Choose a strong, memorable passphrase. You’ll enter this passphrase each time you use the private key (unless using an SSH agent).
Enter passphrase (empty for no passphrase):
Enter same passphrase again:
This generates two files: `id_rsa` (your private key) and `id_rsa.pub` (your public key).
##### Copying Your Public Key to the Ubuntu Server
The most convenient way to copy your public key to the server is using `ssh-copy-id`.
1. Use `ssh-copy-id` (on your local machine):
bash
ssh-copy-id username@your_server_ip
(Add `-p 2222` for a custom port).
You’ll be prompted for your user’s password on the server. This command appends your public key to the `~/.ssh/authorized_keys` file on the server.
2. Manual Copy (if `ssh-copy-id` isn’t available or fails):
a. Copy Public Key to Clipboard (macOS/Linux):
bash
cat ~/.ssh/id_rsa.pub
# Then manually copy the output
Alternatively, using `xclip` or `pbcopy`:
bash
cat ~/.ssh/id_rsa.pub | xclip -selection clipboard # For Linux with xclip
cat ~/.ssh/id_rsa.pub | pbcopy # For macOS
b. Log into Server with Password: Connect using `ssh username@your_server_ip` and your password.
c. Create `.ssh` directory and `authorized_keys` file (if they don’t exist) and set permissions:
bash
mkdir -p ~/.ssh
chmod 700 ~/.ssh
touch ~/.ssh/authorized_keys
chmod 600 ~/.ssh/authorized_keys
d. Append Public Key: Open `authorized_keys` with a text editor and paste your public key string on a new line.
bash
nano ~/.ssh/authorized_keys
Paste the key, save, and exit (Ctrl+X, Y, Enter for Nano).
##### Testing and Disabling Password Authentication
1. Test Key-Based Login:
From your local machine, try to connect again:
bash
ssh username@your_server_ip
If you set a passphrase, you’ll be prompted for it. If successful, you’ve logged in using your key.
2. Disable Password Authentication (Server-Side):
Once you’re confident that key-based authentication works, disable password authentication in `/etc/ssh/sshd_config` to enhance security.
bash
sudo nano /etc/ssh/sshd_config
Find and set:
PasswordAuthentication no
ChallengeResponseAuthentication no
UsePAM no # Sometimes required depending on PAM configuration
Save the file and restart SSH:
bash
sudo systemctl restart ssh
Crucial Warning: Do NOT disable password authentication until you have successfully tested key-based access. Otherwise, you might lock yourself out of your server! Always keep a backup SSH session open or have console access until you’re certain.
2. Change the Default SSH Port
As mentioned earlier, changing `Port 22` to a non-standard port in `/etc/ssh/sshd_config` (e.g., `Port 2222`) can reduce the noise from automated bots scanning for port 22. Remember to update UFW:
bash
sudo ufw allow 2222/tcp
sudo ufw delete allow ssh # To remove the old rule for port 22
sudo systemctl restart ssh
When connecting, always use `ssh -p 2222 username@your_server_ip`.
3. Disable Root Login
Logging in directly as `root` is a security risk because `root` has unrestricted privileges. It’s better to log in as a regular user with `sudo` privileges and then elevate permissions when needed.
In `/etc/ssh/sshd_config`, set:
PermitRootLogin no
Then `sudo systemctl restart ssh`.
4. Restrict SSH Access to Specific Users or Groups
You can explicitly allow or deny users or groups access to SSH.
- Allow Specific Users:
AllowUsers user1 user2
- Allow Specific Groups:
AllowGroups admin_group dev_group
- Deny Specific Users/Groups (less common, usually `Allow` is better):
DenyUsers bad_user
DenyGroups guests
Add these lines to `sshd_config` and restart the service.
5. Implement Fail2Ban for Brute-Force Protection
Fail2Ban is an intrusion prevention framework that scans log files (e.g., `/var/log/auth.log`) for suspicious activity like repeated failed login attempts. Upon detection, it automatically updates firewall rules to temporarily or permanently ban the offending IP address.
1. Install Fail2Ban:
bash
sudo apt install fail2ban
2. Basic Configuration:
The default configuration (`/etc/fail2ban/jail.conf`) is usually sufficient for SSH, but it’s best practice to create a local override.
bash
sudo cp /etc/fail2ban/jail.conf /etc/fail2ban/jail.local
sudo nano /etc/fail2ban/jail.local
Inside `jail.local`, you can adjust settings like:
- `bantime`: How long an IP is banned (e.g., `1h` for 1 hour).
- `findtime`: How long to monitor for failed attempts before a ban (e.g., `10m` for 10 minutes).
- `maxretry`: Number of failed attempts before a ban (e.g., `5`).
Ensure the `[sshd]` section is enabled (usually `enabled = true`). If you changed your SSH port, update `port = ssh` to `port = 2222` (or your custom port).
3. Restart Fail2Ban:
bash
sudo systemctl restart fail2ban
You can check its status with `sudo systemctl status fail2ban`.
Advanced SSH Usage and Techniques
Beyond basic connections, SSH offers powerful features for advanced server management.
1. SSH Agent for Passphrase Management
If you use a passphrase for your SSH private key (highly recommended), you’ll be prompted for it every time you use the key. The SSH agent can store your decrypted private key securely in memory for the duration of your session, requiring the passphrase only once.
- Start the agent (if not running):
bash
eval “$(ssh-agent -s)”
- Add your private key to the agent:
bash
ssh-add ~/.ssh/id_rsa
You’ll be prompted for your passphrase. Once added, subsequent SSH connections using that key won’t require the passphrase until the agent is stopped or restarted.
2. SSH Tunnels (Port Forwarding)
SSH tunnels allow you to securely forward network traffic from one port to another, across the SSH connection. This is invaluable for accessing services on your server that aren’t exposed publicly, or for routing insecure traffic securely.
Local Port Forwarding (Client -> Server -> Destination)
This allows you to access a service running on the server (or another machine reachable by the server) from your local machine, as if it were running on a local port.
bash
ssh -L local_port:destination_host:destination_port username@your_server_ip
Example: Access a web server running on port 80 on your Ubuntu server (only accessible locally on the server) from your local browser on `localhost:8080`.
bash
ssh -L 8080:localhost:80 sammy@your_server_ip
Now, opening `http://localhost:8080` in your local browser will show the content served by your server’s web server.
Remote Port Forwarding (Server -> Client -> Destination)
This allows a remote server to access a service running on your local machine (or another machine reachable by your client), through your client machine. Less common, but useful for exposing a local service to a remote server.
bash
ssh -R remote_port:destination_host:destination_port username@your_server_ip
Example: Allow your server to access a local web service running on your machine at port 3000, through its own port 8000.
bash
ssh -R 8000:localhost:3000 sammy@your_server_ip
Now, on the server, accessing `http://localhost:8000` will connect to `http://localhost:3000` on your client machine.
Dynamic Port Forwarding (SOCKS Proxy)
This turns your SSH client into a SOCKS proxy, allowing applications (like web browsers) to route their traffic through the SSH tunnel. This effectively makes your server act as a proxy for your browsing activity, useful for bypassing geo-restrictions or adding a layer of encryption to potentially insecure local traffic.
bash
ssh -D 8080 username@your_server_ip
Once connected, configure your browser or application to use a SOCKS proxy at `localhost:8080`.
3. SSH Client Configuration File (`~/.ssh/config`)
For frequent connections or complex setups, the client-side SSH configuration file (`~/.ssh/config`) is invaluable. It allows you to define aliases and specific settings for different hosts.
1. Create/Edit the file:
bash
nano ~/.ssh/config
2. Add entries:
Host myserver
Hostname your_server_ip_or_hostname
User sammy
Port 2222
IdentityFile ~/.ssh/id_rsa
ForwardAgent yes # Forward SSH agent to remote server
Host devbox
Hostname 192.168.1.50
User john
Port 22
Now, instead of `ssh -p 2222 sammy@your_server_ip -i ~/.ssh/id_rsa`, you can simply type `ssh myserver`.
4. SSH Multiplexing (ControlMaster)
Multiplexing allows multiple SSH sessions to share a single underlying SSH connection. This speeds up subsequent connections as they don’t need to re-authenticate, and it can be useful for SCP/SFTP while maintaining an open shell.
Add these to your `~/.ssh/config` file, usually under a `Host *` or specific `Host` entry:
Host *
ControlMaster auto
ControlPath ~/.ssh/control/%r@%h:%p
ControlPersist 10m # Keep the master connection open for 10 minutes after last client closes
The `ControlPath` specifies where the control socket file will be created. Make sure the directory `~/.ssh/control` exists (`mkdir -p ~/.ssh/control`).
Now, when you open an SSH connection, it will create a master connection. Subsequent `ssh`, `scp`, or `sftp` commands to the same host will reuse this master connection.
Troubleshooting Common SSH Issues
Even with careful setup, you might encounter issues. Here are some common problems and their solutions.
1. “Connection Refused”
- Firewall: The most common cause. Check if UFW (or another firewall) is blocking port 22 (or your custom port) on the server: `sudo ufw status`. Allow it: `sudo ufw allow ssh` or `sudo ufw allow 2222/tcp`.
- SSH Service Not Running: Check the SSH service status on the server: `sudo systemctl status ssh`. Start it if necessary: `sudo systemctl start ssh`.
- Incorrect Port: Ensure you’re connecting to the correct port (default 22, or your custom port with `-p`).
- `sshd_config` Errors: Check `/var/log/auth.log` or `journalctl -u ssh` on the server for errors after restarting `sshd`.
2. “Permission Denied (publickey, password)”
- Incorrect Username/Password: Double-check your username and password.
- Incorrect Key Permissions (Local): Your private key file (`~/.ssh/id_rsa`) must have strict permissions: `chmod 600 ~/.ssh/id_rsa`.
- Incorrect Key Permissions (Server): The `~/.ssh` directory on the server must be `chmod 700`, and `~/.ssh/authorized_keys` must be `chmod 600`.
- `sshd_config` Disallows Method: If you’ve disabled `PasswordAuthentication` or `PermitRootLogin`, ensure you’re using the correct authentication method or user.
- Key Not in `authorized_keys`: Verify your public key is correctly appended to `~/.ssh/authorized_keys` on the server.
- SELinux/AppArmor: In rare cases, security modules like SELinux or AppArmor might interfere. Check their logs for denials.
- Verbose Output: Connect with `ssh -v username@ip` for verbose debugging output, which can often pinpoint the exact issue.
3. “Host key verification failed”
This means the host key presented by the server does not match the one stored in your `~/.ssh/known_hosts` file.
- Legitimate Server Change: The server might have been reinstalled, its IP changed, or its SSH host key regenerated. If you’re certain it’s legitimate, you can remove the old entry:
bash
ssh-keygen -R your_server_ip_or_hostname
Then reconnect, accept the new fingerprint.
- Man-in-the-Middle Attack: This is a severe warning. If you’re unsure, do *not* proceed. Investigate the server’s identity through an out-of-band method.
Conclusion: Your Secure Gateway to Ubuntu Server Management
SSH is an indispensable tool for managing Ubuntu servers, providing a secure and versatile platform for remote administration, file transfers, and secure tunneling. By understanding its foundational components, mastering its practical commands, and diligently implementing security best practices, you empower yourself with the control and peace of mind necessary for effective server operation.
From initial setup and firewall configuration to the critical shift towards SSH key authentication and the deployment of advanced techniques like port forwarding and `~/.ssh/config`, this guide has furnished you with a comprehensive understanding. Always prioritize security, regularly update your systems, and audit your configurations to ensure your Ubuntu server remains a robust and well-protected asset in your digital infrastructure.