The Persistent Enigma of Dropping SSH Connections
In the vast and interconnected landscape of modern computing, the Secure Shell (SSH) protocol stands as a ubiquitous, indispensable conduit. It is the digital lifeline that grants developers, system administrators, and tech enthusiasts secure access to remote servers, enabling everything from critical system maintenance to the deployment of complex applications. Yet, for all its robustness and security, there’s a shared groan that echoes across the digital trenches: the SSH connection that inexplicably, frustratingly, keeps disconnecting.
This isn’t merely an inconvenience; it’s a productivity killer, a workflow disruptor, and a source of profound exasperation. Imagine meticulously crafting a complex command, only for the session to drop mid-execution, leaving you to restart from scratch. Or attempting a critical deployment, only to be met with a “Connection reset by peer” error at a pivotal moment. These intermittent disconnections transform a seamless workflow into a fragmented, stressful ordeal.
Navigating the Digital Lifeline: Why SSH Matters
At its core, SSH provides a cryptographic network protocol for operating network services securely over an unsecured network. It’s the secure gateway to countless servers, cloud instances, and IoT devices worldwide. Beyond simple command-line access, SSH tunnels facilitate secure data transfer, port forwarding, and the secure execution of remote graphical applications. Its foundational role in development operations, system administration, and cloud infrastructure cannot be overstated. When this critical link becomes unreliable, the entire edifice of remote management begins to wobble.
The Shared Frustration: A Universal Challenge
The problem of dropping SSH connections is remarkably common, transcending specific operating systems, network configurations, or server types. It’s a challenge that unites users across diverse technological ecosystems. The difficulty lies in its multifaceted nature: a disconnection can stem from an issue on the client machine, a fault on the remote server, an unstable element within the sprawling network path between them, or even a subtle misconfiguration that evades immediate detection.
This article aims to unravel the complexities behind these frustrating disconnections. Acting as an expert guide, we will embark on a comprehensive diagnostic journey, dissecting the myriad causes and providing actionable solutions. From the subtle nuances of client-side settings to the robust configurations of server daemons and the intricacies of network topology, we will explore every facet. Our goal is not just to offer quick fixes but to empower you with the knowledge to systematically diagnose, understand, and ultimately conquer the persistent enigma of dropping SSH connections, ensuring your digital lifeline remains steadfast and unbroken.
Deconstructing the Disconnect: Understanding SSH’s Vulnerabilities
To effectively troubleshoot a problem, one must first understand the underlying mechanisms that govern its behavior. SSH, while designed for resilience, operates within a dynamic environment where countless variables can impact its stability. Understanding how an SSH session is maintained—and subsequently, how it can be disrupted—is the cornerstone of effective diagnosis and resolution.
The Protocol’s Foundation: How SSH Stays Alive
An SSH connection is essentially a persistent TCP/IP socket established between a client and a server, secured with encryption and authentication. Once established, the client and server exchange data packets over this secure tunnel. For the connection to remain active, both ends must implicitly or explicitly acknowledge the continued presence of the other.
Typically, as long as data is being transmitted—whether user input, command output, or background processes—the underlying TCP connection remains active. However, prolonged periods of inactivity introduce vulnerabilities. Network devices (routers, firewalls) often employ session timeouts to conserve resources, dropping idle connections after a certain duration. Similarly, operating systems might reclaim resources associated with seemingly defunct connections. The SSH protocol itself, by default, does not send periodic “keepalive” messages, relying instead on the activity of the user or applications within the session. This reliance on active data flow is a key vulnerability point.
The Delicate Dance: What Can Go Wrong
The reasons an SSH session might terminate unexpectedly are diverse, broadly categorized into three main areas: client-side issues, server-side issues, and network-related problems.
Client-Side Factors: These originate from your local machine or its immediate environment. They can include an unstable local network, a misconfigured SSH client, an overloaded local system, or even issues with your terminal emulator. The client might mistakenly believe the server has dropped the connection or suffer its own local network disruption.
Server-Side Factors: Problems on the remote host can equally lead to disconnections. An overloaded server struggling with CPU, memory, or disk I/O could fail to respond to the client. The SSH daemon (sshd) might be misconfigured, or the server’s firewall could be dropping packets. Even operating system-level events, like an Out-Of-Memory (OOM) killer terminating `sshd`, can cause abrupt session loss.
Network-Related Interventions: Often the most elusive culprits, network issues lie between your client and the server. This could involve an overloaded intermediate router, a firewall with aggressive session timeout policies, an unstable VPN connection, or even issues at your Internet Service Provider (ISP). Packet loss, high latency, and Maximum Transmission Unit (MTU) mismatches can all contribute to dropped connections without clear error messages.
The challenge lies in the fact that the symptom—a dropped SSH connection—is singular, but the underlying causes are manifold. This necessitates a systematic and comprehensive diagnostic approach, which we will now explore.
A Diagnostic Journey: Pinpointing the Culprit
Diagnosing the precise reason for a dropping SSH connection requires a methodical approach, much like a forensic investigation. Jumping to conclusions or randomly applying fixes can waste time and obscure the actual problem. The goal is to gather evidence from all potential sources—client, server, and network—to narrow down the possibilities.
Initial Reconnaissance: Quick Checks and Obvious Offenders
Before diving into complex logs and network tools, rule out the simplest possibilities.
1. Check Local Internet Connectivity: Is your own internet connection stable? Can you browse websites, access other services? A flaky local Wi-Fi or wired connection is a surprisingly common culprit.
2. Test Other SSH Connections: Can you SSH to other servers without issues? If so, the problem is likely specific to the problematic server or the network path leading to it. If all SSH connections are unstable, your local setup or ISP is more likely the issue.
3. Monitor Server Uptime/Status: Is the remote server itself experiencing an outage or heavy load? Check monitoring tools (if available) or try pinging the server to see if it responds consistently.
4. Try a Different Client/Network: If possible, attempt to connect from a different computer or a different network (e.g., using a mobile hotspot) to the problematic server. This helps isolate if the issue is with your client machine or local network.
5. Restart Router/Modem: For local network issues, a simple restart of your home or office router can sometimes resolve transient problems.
Delving into Logs: The Digital Breadcrumbs
Logs are invaluable for understanding what transpired just before a disconnection. They provide a narrative of events from the perspective of both the client and the server.
Client-Side Traces: Unpacking SSH Client Output
Your SSH client can be configured to be more verbose, revealing details about the connection process and any errors encountered.
To enable verbose output, add `-v`, `-vv`, or `-vvv` to your SSH command:
`ssh -vvv user@your_server_ip`
- `-v` (verbose): Shows general progress and warning messages.
- `-vv` (very verbose): Adds debug messages about authentication, configuration, and connection setup.
- `-vvv` (debug level 3): Provides the most detailed output, including packet exchanges and cryptographic details. This can be overwhelming but is crucial for deep dives.
Look for messages like:
- `debug1: Connection to XXX.XXX.XXX.XXX port 22 GAVE UP.`
- `Broken pipe`
- `Connection reset by peer`
- `Bad packet length`
- `Remote host closed connection`
- `Read from remote host XXX.XXX.XXX.XXX: Connection reset by peer`
These messages, combined with the context of the verbose output, can often indicate whether the client initiated the disconnect, or if the server or an intermediary device closed the connection.
Server-Side Chronicles: Scrutinizing Auth.log and Syslog
On the remote server, the SSH daemon’s activities are logged, providing critical insights into why it might have terminated a session.
The primary log files to check (locations might vary slightly depending on the Linux distribution):
- `/var/log/auth.log` (Debian/Ubuntu): Contains authentication attempts, successful logins, and SSH daemon activity.
- `/var/log/secure` (CentOS/RHEL/Fedora): Similar to `auth.log`, focusing on security-related events.
- `/var/log/syslog` (General Linux): A more general system log that might also contain SSH-related messages, especially if `sshd` encounters a system-level error.
Use `grep` to filter for SSH-related entries:
`sudo grep sshd /var/log/auth.log | tail -n 50`
`sudo grep sshd /var/log/secure | tail -n 50`
Look for entries indicating:
- Session closed: `session closed for user `
- Authentication failures: (While not directly a disconnection cause, repeated failures could indicate an attack or misconfiguration that might stress `sshd`).
- `sshd` crashes or restarts: If the daemon itself is crashing, that’s a major clue.
- Messages from the OOM killer: `Out of memory: Kill process (sshd)` – this is a definitive server-side problem.
- Warnings about `MaxStartups` or `MaxSessions`: These indicate the server is refusing new connections due to resource limits.
Network Forensics: Tracing the Interconnect
Network issues are often the most challenging to diagnose because they occur “in between” the client and server. However, several tools can help visualize the network path and identify points of failure.
Ping and Traceroute: Basic Network Health Checks
- `ping `: This basic utility sends ICMP echo requests to the server and measures round-trip time (latency) and packet loss.
- High latency: Suggests network congestion or a distant server.
- Packet loss: Indicates network instability, potentially leading to dropped SSH connections. Even 1-2% packet loss can destabilize an SSH session.
- Intermittent timeouts: A strong indicator of network issues.
- `traceroute ` (Linux/macOS) / `tracert ` (Windows): This command shows the path (hops) packets take to reach the server. It can help identify where latency spikes or packet loss begins along the route.
- Look for specific hops that consistently show high latency or timeouts. This could point to an overloaded router or a firewall blocking ICMP.
MTR: The Advanced Network Detective
`MTR` (My Traceroute) is a powerful network diagnostic tool that combines the functionality of `ping` and `traceroute` into a single, continuously updating output. It provides a real-time view of packet loss and latency at each hop along the path.
`mtr `
- `MTR` continuously sends packets and updates statistics for each hop, making it excellent for identifying intermittent network problems that `ping` or `traceroute` might miss.
- Focus on the `Loss%` column for each hop. If loss starts appearing at a specific hop and persists through subsequent hops, that hop (or the network segment immediately after it) is likely the source of the problem.
- High latency at specific hops, especially when combined with packet loss, is a strong indicator of network congestion or an issue with that particular router.
By systematically working through these diagnostic steps, gathering evidence from client logs, server logs, and network tools, you can significantly narrow down the potential causes of your dropping SSH connections, paving the way for targeted and effective solutions.
Fortifying the Client-Side: Empowering Your Local Machine
Often, the solution to persistent SSH disconnections lies closer to home than you might think. Modifying your local SSH client configuration, addressing local network instabilities, or managing your terminal environment can dramatically improve connection resilience.
Client-Side Keepalives: Bypassing Idle Timeouts
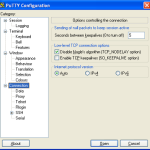
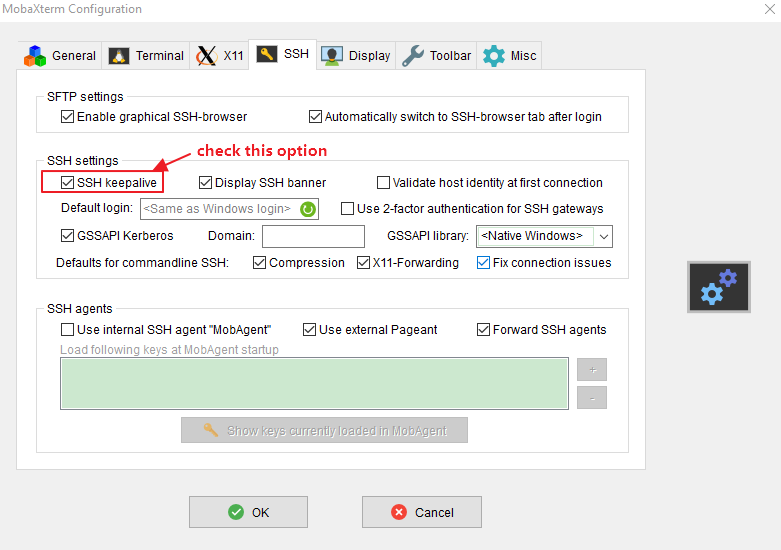
One of the most common reasons for SSH disconnections is network devices or firewalls terminating idle TCP connections. Client-side keepalives address this by periodically sending null packets from the client to the server, signaling that the connection is still active.
`ServerAliveInterval` and `ServerAliveCountMax` Explained
These two directives in your client’s SSH configuration are your primary tools for client-side keepalives.
- `ServerAliveInterval`: This directive specifies the time in seconds after which the client will send a null packet to the server if no data has been received from the server. This packet, often called a “keepalive” or “null packet,” serves to keep the TCP connection alive and prevent firewalls from timing it out.
- Where to set it: You can add this to your global SSH configuration file (`~/.ssh/config` for specific hosts, or `/etc/ssh/ssh_config` for all connections) or directly as a command-line option (`-o ServerAliveInterval=X`).
- Recommended Value: A common starting point is `60` seconds (1 minute) or `30` seconds, especially if you experience frequent disconnects. This is less aggressive than some server-side settings but generally sufficient.
- Example in `~/.ssh/config`:
Host my_server
Hostname your_server_ip
User your_username
ServerAliveInterval 60
ServerAliveCountMax 3
- Example on command line:
`ssh -o ServerAliveInterval=60 user@your_server_ip`
- `ServerAliveCountMax`: This specifies the number of server alive messages (as configured by `ServerAliveInterval`) which may be sent without `sshd` responding. If this threshold is reached while server alive messages are being sent, SSH will disconnect from the server, assuming it has crashed or the network connection has failed.
- Recommended Value: `3` is a common and sensible default. This means if the server fails to respond to 3 consecutive keepalives (e.g., after 3 minutes if `ServerAliveInterval` is 60s), the client will gracefully terminate the session. Setting it too high might make the client wait too long for a truly dead server, while too low might cause premature disconnections on very flaky networks.
Important Note: These `ServerAlive` directives are distinct from TCP keepalives, which operate at a lower layer of the networking stack. SSH’s `ServerAlive` is application-level and is generally more effective for preventing mid-session disconnects caused by idle timeouts.
Mitigating Local Network Instability
Your immediate network environment can be a significant source of instability.
Wi-Fi Woes and VPN Vagaries
- Unstable Wi-Fi: Wireless networks are inherently more susceptible to interference, signal degradation, and packet loss than wired connections.
- Solution: If possible, switch to a wired (Ethernet) connection. If not, try moving closer to your Wi-Fi router, reducing interference from other devices, or ensuring your router firmware is up to date.
- Flaky VPN Connections: If you’re connecting to SSH via a VPN, the VPN itself might be the weak link.
- Solution: Test SSH without the VPN (if secure and feasible). Ensure your VPN client and server are configured correctly and that your VPN provider is stable. Some VPNs have their own idle timeout settings that can interfere. Check your VPN logs for disconnection events.
- Local Firewall/Antivirus: Occasionally, an overzealous local firewall or antivirus program might inspect or interfere with SSH traffic, leading to dropped connections.
- Solution: Temporarily disable them for testing (with caution!) or ensure SSH traffic (port 22, or custom port) is explicitly allowed.
Addressing Terminal and SSH Agent Peculiarities
Sometimes, the issue isn’t the network or SSH itself, but the tools interacting with it.
Terminal Emulator Configuration
Different terminal emulators (e.g., PuTTY, iTerm2, Kitty, Windows Terminal, xterm) can have their own nuances.
- Scrollback Buffer Issues: Some emulators, particularly older ones or those on resource-constrained systems, might struggle with large amounts of scrollback data, potentially leading to slowdowns or perceived freezes that look like disconnections.
- Solution: Try a different terminal emulator, or reduce the scrollback buffer size.
- Encoding Mismatches: Incorrect character encoding can lead to garbled output, which might sometimes manifest as issues that break the session, though this is less common for full disconnections.
- Solution: Ensure both your client and server are using compatible encodings (usually UTF-8).
SSH Agent Forwarding and Key Management
While less common for *disconnections*, issues with SSH agent forwarding can cause authentication problems that *prevent* connections or lead to a prompt asking for your password repeatedly, which might be mistaken for an unstable connection.
- Ensure `ssh-agent` is running and keys are loaded: `ssh-add -l` should list your loaded keys.
- Avoid excessive forwarding: While convenient, agent forwarding can sometimes be a security risk and, in rare cases, might contribute to complexity that masks other issues.
By diligently configuring client-side keepalives, stabilizing your local network, and ensuring your terminal environment is robust, you can significantly enhance the resilience of your SSH connections from your end.
Reinforcing the Server-Side: Stabilizing the Remote Host
Even with a perfectly configured client and a stable local network, problems on the remote server can still lead to frustrating disconnections. Server-side issues often involve resource exhaustion, misconfigured daemon settings, or firewall rules inadvertently blocking traffic.
Server-Side Keepalives: Sustaining the Session
Just as the client can send keepalives, the SSH server (sshd) can also be configured to periodically check if the connected client is still responsive. This is often a more robust solution, as the server is typically more stable than the client machine.
`ClientAliveInterval` and `ClientAliveCountMax` in `sshd_config`
These directives are configured in the `sshd_config` file on the remote server (typically located at `/etc/ssh/sshd_config`).
- `ClientAliveInterval`: Specifies the time in seconds that the `sshd` daemon will wait before sending a null packet to the client if no data has been received from the client. This helps detect dead clients or network interruptions between the client and server.
- Recommended Value: `60` seconds (1 minute) is a common and effective setting. You might go lower (e.g., `30`) for very aggressive network timeouts, but excessively low values can generate more network traffic.
- `ClientAliveCountMax`: This specifies the number of client alive messages (as configured by `ClientAliveInterval`) which may be sent without `sshd` receiving any messages back from the client. If this threshold is reached, `sshd` will disconnect the client, assuming it has died or the network connection has failed.
- Recommended Value: `3` or `5` are common. A value of `3` means if `ClientAliveInterval` is `60`, the server will terminate the connection after 3 * 60 = 180 seconds (3 minutes) of unresponsiveness from the client.
Example in `/etc/ssh/sshd_config`:
ClientAliveInterval 60
ClientAliveCountMax 3
After making changes to `sshd_config`, you MUST restart the SSH daemon for them to take effect:
`sudo systemctl restart sshd` (for systemd-based systems like Ubuntu 16.04+, CentOS 7+)
`sudo service sshd restart` (for older sysvinit-based systems)
Caution: Modifying `sshd_config` incorrectly can lock you out of your server. Always have a backup way to access the server (e.g., through a cloud provider’s console access) before making changes.
Resource Management: Preventing Server Exhaustion
A server struggling with resource scarcity is a frequent cause of intermittent disconnections. When the server becomes unresponsive, the client interprets this as a dropped connection.
CPU, Memory, and Disk I/O Bottlenecks
- High CPU Usage: A server with 100% CPU utilization may become unresponsive, leading to SSH timeouts.
- Diagnosis: Use `top`, `htop`, `vmstat`, `sar` to monitor CPU load.
- Solution: Identify and optimize resource-intensive processes, scale up server resources, or offload tasks.
- Memory Exhaustion: Running out of RAM can cause the kernel to swap excessively (which is slow) or, worse, invoke the Out-Of-Memory (OOM) killer.
- Diagnosis: Use `free -h`, `htop`, `vmstat`. Check `/var/log/kern.log` or `syslog` for OOM killer messages.
- Disk I/O Bottlenecks: Heavy disk activity can make the server slow to respond to requests, including SSH traffic.
- Diagnosis: Use `iostat`, `iotop`. Look for high I/O wait times.
- Solution: Optimize disk-intensive applications, use faster storage (SSDs), or distribute load.
The OOM Killer: A Silent Assassin
The Linux kernel’s Out-Of-Memory (OOM) killer is designed to prevent system crashes by terminating processes when memory is critically low. If `sshd` or a related process is targeted by the OOM killer, your SSH session will abruptly terminate.
- Diagnosis: Check `dmesg` output or `syslog`/`kern.log` for messages like `Out of memory: Kill process (sshd)`.
- Solution: Increase server RAM, reduce memory footprint of other applications, or ensure `sshd` has a high OOM score adjustment (`oom_score_adj`) to make it less likely to be killed.
Firewall and Security Group Scrutiny
Server-side firewalls (e.g., `ufw`, `firewalld`, `iptables`) or cloud provider security groups (e.g., AWS Security Groups, Azure Network Security Groups) can mistakenly block or prematurely terminate SSH connections.
- Inbound and Outbound Rules: Ensure that inbound TCP traffic on your SSH port (default 22) is allowed from your client’s IP address range. Also, verify that outbound traffic from the server is not being blocked, as this could prevent the server from sending responses back to your client.
- Connection Tracking Timeouts: Some firewalls have aggressive connection tracking timeouts that can drop idle connections faster than SSH’s keepalives.
- Solution: Adjust firewall timeout settings if you have control, or rely more heavily on SSH’s `ClientAliveInterval`.
- Rate Limiting: Firewalls might implement rate limiting for connection attempts. While usually for preventing brute-force attacks, misconfigurations could affect legitimate connections, though typically leading to connection rejections rather than mid-session drops.
SSH Daemon Configuration Nuances
Beyond keepalives, other `sshd_config` settings can influence stability.
- `MaxStartups`: Limits the number of concurrent unauthenticated connections. If too low, legitimate new connection attempts might be dropped, appearing as a failure to connect rather than a disconnection.
- `MaxSessions`: Limits the number of open shell, login or subsystem sessions permitted per network connection. If reached, new sessions within an existing connection might be rejected.
- `UseDNS no`: By default, `sshd` might try to resolve the client’s IP address to a hostname for logging. If your DNS server is slow or unreliable, this lookup can introduce delays or even timeouts, making the connection appear unresponsive. Setting `UseDNS no` can sometimes improve connection stability and speed.
- `TCPKeepAlive yes`: This enables standard TCP keepalives (at the operating system level, below SSH). While generally less effective than `ClientAliveInterval` for SSH-specific idle timeouts, it can provide an additional layer of resilience against network failures where a TCP connection silently dies.
By carefully configuring server-side keepalives, diligently monitoring server resources, and ensuring your firewalls and `sshd` settings are optimized, you can build a much more robust and stable remote host environment for your SSH sessions.
Bridging the Gap: Network-Related Solutions
When client and server are seemingly well-behaved, the culprit often resides within the labyrinthine network infrastructure spanning between them. These intermediate devices and services can introduce packet loss, latency, or aggressive session management that terminates SSH connections prematurely.
MTU Issues: The Packet Size Predicament
The Maximum Transmission Unit (MTU) defines the largest size of a packet that can be transmitted over a network. An MTU mismatch along the network path can lead to packet fragmentation, retransmissions, or even black-holing (where packets are dropped without notification), all of which can severely disrupt an SSH session.
Understanding Path MTU Discovery
Path MTU Discovery (PMTUD) is a mechanism that dynamically determines the smallest MTU along the entire network path between two hosts. If PMTUD fails (e.g., due to an intermediate firewall blocking ICMP “fragmentation needed” messages), packets larger than a certain MTU might be dropped.
- Diagnosis: Symptoms include SSH sessions freezing after a period of inactivity or after sending large amounts of data, or connections failing during file transfers (`scp`). The `ping` command with the “do not fragment” flag can help:
`ping -M do -s 1472 ` (Linux/macOS)
`ping -f -l 1472 ` (Windows)
Gradually reduce the payload size (1472 is typical for 1500 MTU minus ICMP header) until packets stop dropping.
- Solution:
- Client-side: Lower your client’s interface MTU if you consistently connect over a problematic path.
- Server-side: Ensure the server’s network interface MTU is set correctly (typically 1500 for Ethernet, or 1400-1450 for VPNs/tunnels).
- Firewall/Router: Verify that ICMP type 3 code 4 (“fragmentation needed”) messages are not being blocked by any firewalls along the path.
Intermediate Network Devices: Routers, Firewalls, and Proxies
The journey of an SSH packet often involves traversing multiple routers, firewalls, and potentially proxy servers, each of which can introduce points of failure.
Session Timeouts and Connection Tracking
Many network devices maintain “connection tracking” tables to keep track of active network sessions. To conserve resources, these devices implement aggressive idle session timeouts. If an SSH connection remains idle for longer than the device’s timeout, it will simply drop the connection, even if SSH’s own keepalives are active.
- Diagnosis: If SSH `ServerAliveInterval` or `ClientAliveInterval` are set higher than the firewall’s timeout, the connection will drop. These timeouts are often found on corporate firewalls, NAT routers, or cloud provider network gateways.
- Solution: Increase the frequency of SSH keepalives (both `ServerAliveInterval` and `ClientAliveInterval`) to be *shorter* than the shortest known or suspected network timeout. For example, if a firewall times out after 5 minutes (300 seconds), set `ServerAliveInterval` and `ClientAliveInterval` to 60 seconds.
Deep Packet Inspection and Its Impact
Some corporate networks or ISPs employ Deep Packet Inspection (DPI) for security, traffic shaping, or content filtering. While rare, DPI engines can sometimes interfere with encrypted SSH traffic, leading to dropped connections or performance degradation.
- Diagnosis: This is difficult to confirm without access to the network device. If disconnections only occur on specific networks with known DPI policies, it’s a possibility.
- Solution: Often, there’s no direct fix other than connecting from a different network or using a VPN *before* SSH (which might bypass the DPI, but introduces its own set of potential issues).
ISP and VPN Instabilities: Beyond Your Control, Within Your Influence
Your Internet Service Provider (ISP) and any VPN services you use represent significant segments of the network path over which you have limited direct control, but their stability is paramount.
- ISP-Related Disconnections: ISPs can have their own network issues, including congestion, routing problems, or transient outages.
- Diagnosis: Use `ping` and `MTR` to external, stable services (like Google DNS: 8.8.8.8) to check for general ISP instability. Check with your ISP for known outages in your area.
- Solution: Report issues to your ISP. If persistent, consider switching providers or using a secondary internet connection (e.g., mobile hotspot) as a fallback.
- VPN Instability and Configuration: If you’re using a VPN, the VPN tunnel itself is a critical network link. A weak or unstable VPN connection will inevitably lead to SSH disconnections.
- Diagnosis: Check VPN client logs for connection drops or errors. Monitor VPN connection status.
- Solution: Ensure your VPN client is up-to-date. Try connecting to a different VPN server or protocol (e.g., OpenVPN instead of IKEv2). Verify VPN server load. For self-hosted VPNs, ensure sufficient server resources and optimal configuration. Sometimes, configuring TCP instead of UDP for the VPN protocol can offer more stability, albeit with slightly higher overhead.
By meticulously examining the network path with tools like `ping`, `traceroute`, and `MTR`, and understanding how intermediate devices and services can impact session stability, you can often identify and mitigate the network-related factors contributing to SSH disconnections.
Advanced Strategies for Uninterrupted Connectivity
While addressing the root causes through systematic diagnosis is paramount, there are also advanced tools and configurations that can inherently make your SSH sessions more resilient, especially when operating over inherently unstable networks. These strategies focus on maintaining session state or creating connections that are designed to withstand transient interruptions.
Mosh: The Mobile Shell for Imperfect Networks
Mosh (Mobile Shell) is a groundbreaking alternative to SSH designed specifically for unreliable connections, intermittent network access, and mobile usage. It offers several key advantages over traditional SSH:
- Roams Seamlessly: Mosh can transparently switch between different IP addresses, meaning you can move your laptop from Wi-Fi to cellular, or change Wi-Fi networks, without losing your shell session.
- Survives Disconnections: Instead of dropping your session when the network goes down, Mosh maintains the session state on the server. When network connectivity is restored, your terminal immediately reflects the current state of the server session.
- Responsive Local Echo: Mosh uses a state synchronization protocol that provides immediate local echo of keystrokes, even on high-latency connections, making the shell feel much more responsive than SSH.
- Adaptive to Bandwidth: It can dynamically adjust to network bandwidth fluctuations.
How it Works: Mosh operates over UDP (by default, port 60000-60010) rather than TCP. It initiates an SSH connection to set up the session and exchange keys, but then switches to its own UDP-based protocol for actual data transfer.
Usage:
1. Install Mosh on both client and server: `sudo apt install mosh` (Debian/Ubuntu) or `sudo yum install mosh` (CentOS/RHEL).
2. Ensure UDP ports (e.g., 60000-60010) are open on your server’s firewall.
3. Connect using `mosh user@your_server_ip`.
Considerations: Mosh does not support SSH agent forwarding or port forwarding directly; you still need a traditional SSH connection for those specific functionalities. However, for interactive shell access over challenging networks, Mosh is unparalleled.
Session Management with `tmux` and `screen`
For critical, long-running processes or simply to maintain your work context across disconnections (even planned ones), session multiplexers like `tmux` (Terminal Multiplexer) and `screen` are indispensable.
How they help: These tools allow you to start a session on the remote server that persists even if your SSH client disconnects. You can detach from a session, disconnect your SSH client, and later reattach to the *same running session* from a new SSH connection, picking up exactly where you left off. This makes SSH disconnections largely irrelevant to the continuity of your work.
Key Features:
- Persistent Sessions: Applications run within `tmux`/`screen` continue to execute even after your SSH client disconnects.
- Multiple Windows/Panes: Manage multiple terminal windows or split panes within a single session, enhancing productivity.
- Shared Sessions: Multiple users can attach to the same `tmux`/`screen` session, facilitating collaborative work.
Basic Usage:
1. SSH into your server.
2. Start a new `tmux` session: `tmux new -s my_session` (or just `tmux` for an unnamed session).
3. Do your work.
4. To detach: Press `Ctrl+b` then `d` (for `tmux`) or `Ctrl+a` then `d` (for `screen`). Your SSH session can now be safely disconnected.
5. To reattach: `tmux attach -t my_session` (or `tmux attach` for the last session) after reconnecting via SSH.
Recommendation: `tmux` is generally considered more modern and feature-rich than `screen`, but both achieve the core goal of session persistence. Learn one and incorporate it into your daily workflow.
Optimizing SSH Configuration for Resilience
Beyond the basic keepalives, a few other SSH configuration tweaks can subtly improve resilience:
- `IPQoS lowdelay` (Client-side `~/.ssh/config`): This setting requests the underlying TCP connection to prioritize low delay. While network devices might ignore QoS requests, it can sometimes help on congested networks.
Host *
IPQoS lowdelay
- `HostKeyAlgorithms` and `KexAlgorithms` (Client/Server): Ensure you’re using modern, efficient cryptographic algorithms. While not directly preventing disconnections, using well-performing algorithms can reduce computational overhead, potentially improving responsiveness on resource-constrained systems or during heavy traffic. Avoid deprecated algorithms.
- `Compression yes` (Client-side `~/.ssh/config`): For very slow links, enabling compression can sometimes make the connection feel more responsive by reducing the amount of data transferred. However, on fast links, the overhead of compression/decompression can sometimes make it slower. Test to see if it helps your specific scenario.
Proactive Monitoring: Staying Ahead of Disconnections
The best defense is often a good offense. Implementing server monitoring can help you identify resource bottlenecks or daemon issues *before* they lead to SSH disconnections.
- Resource Monitoring: Tools like Prometheus + Grafana, Netdata, Zabbix, or even simple scripts that log `top`/`free` output can track CPU, memory, disk I/O, and network usage. Set up alerts for high utilization.
- Log Monitoring: Centralized log management (e.g., ELK stack, Splunk, LogDNA) can aggregate and analyze `auth.log` or `syslog` entries, alerting you to `sshd` crashes, OOM killer invocations, or repeated authentication failures.
- Uptime Monitoring: External uptime monitoring services can periodically check if your SSH port is open and responsive, giving you an early warning if the server becomes unreachable.
By adopting these advanced strategies, from employing specialized tools like Mosh and `tmux` to fine-tuning your SSH configurations and proactively monitoring your server’s health, you can build an incredibly robust and resilient SSH workflow, transforming the frustrating experience of disconnections into a manageable and often entirely avoidable inconvenience.
Conclusion: Mastering the Art of Persistent SSH
The journey through the intricate world of dropping SSH connections reveals a complex interplay of client configurations, server health, and network dynamics. What initially appears as a single, frustrating symptom is, in reality, a diagnostic puzzle with myriad potential solutions. From subtle Wi-Fi fluctuations to aggressive firewall timeouts and server resource starvation, each piece contributes to the grand tapestry of digital instability.
The Systematic Approach: Your Best Defense
The overarching lesson is the indispensable value of a systematic, methodical approach to troubleshooting. Rather than resorting to guesswork, start with the basics:
1. Verify local connectivity.
2. Examine verbose client logs for immediate clues.
3. Scrutinize server logs for daemon-level events and resource issues.
4. Perform network diagnostics with `ping`, `traceroute`, and `MTR` to map the path and pinpoint network weaknesses.
Once the diagnostic evidence points towards a particular area—be it client, server, or network—then, and only then, can targeted solutions be effectively applied. Configure client-side `ServerAliveInterval` and `ServerAliveCountMax` for local resilience. Fortify the server with `ClientAliveInterval` and diligent resource management. Bridge network gaps by adjusting MTU, understanding firewall timeouts, and ensuring VPN stability.
A Commitment to Stability: The Ongoing Endeavor
Beyond reactive troubleshooting, embracing proactive measures is key. Integrating tools like Mosh for mobile resilience and `tmux` or `screen` for session persistence transforms disconnections from critical workflow interruptions into mere blips. Regularly reviewing SSH configurations, monitoring server performance, and maintaining up-to-date software contribute significantly to a stable and secure SSH environment.
Mastering the art of persistent SSH is not about finding a single magic bullet; it’s about developing an informed understanding of the entire ecosystem. It’s about combining meticulous diagnostics with intelligent configuration and the adoption of resilient tools. By doing so, you can ensure that your digital lifeline remains steadfast, allowing you to focus on innovation, development, and critical system management without the constant dread of an unexpected “Connection reset by peer.” May your SSH sessions be long, stable, and profoundly productive.