The In-Depth OpenSSH Troubleshooting Guide: Navigating Connection & Authentication Challenges
OpenSSH, the ubiquitous suite of secure networking utilities, forms the backbone of countless secure remote administration and file transfer operations worldwide. From managing cloud instances to accessing local servers, its reliability is paramount. However, even the most robust systems encounter anomalies, and OpenSSH is no exception. When a seemingly straightforward `ssh` command fails, it can halt critical workflows and induce significant frustration. This comprehensive guide aims to equip IT professionals, system administrators, and developers with an advanced, systematic approach to diagnosing and resolving the most common, and some less common, OpenSSH issues.
This article transcends basic “check-your-password” advice, delving into the intricate layers of network connectivity, server configuration, client settings, and authentication mechanisms. We will explore a methodical troubleshooting framework, dissecting common error messages, and providing actionable solutions underpinned by a deep understanding of OpenSSH’s operational intricacies. Our objective is to transform a puzzling `ssh` failure into a solvable technical challenge, enhancing your proficiency and minimizing downtime.
Understanding the OpenSSH Ecosystem: A Prerequisite for Diagnosis
Before diving into specific troubleshooting steps, it’s essential to grasp the fundamental components and their interactions within the OpenSSH ecosystem. A clear understanding of what’s supposed to happen provides a baseline against which to measure deviations.
OpenSSH operates on a client-server model. The SSH client (typically `ssh` on your local machine) initiates a connection, while the SSH daemon (`sshd`) on the remote server listens for and responds to these connection attempts.
Core Components and Their Roles
- SSH Client (`ssh`): Your local command-line tool. It reads its configuration from `~/.ssh/config` or `/etc/ssh/ssh_config` and uses private keys from `~/.ssh/`.
- SSH Daemon (`sshd`): The server-side process that listens for incoming SSH connections, handles authentication, and manages secure sessions. Its primary configuration file is `/etc/ssh/sshd_config`.
- Configuration Files:
- `sshd_config`: Controls the server’s behavior (ports, authentication methods, user restrictions, logging).
- `ssh_config` (client-side): Influences how the client behaves (default user, preferred authentication, specific host configurations).
- `authorized_keys` (server-side, per-user): Contains public keys allowed to authenticate as a specific user.
- Key Files:
- Private Keys: Stored on the client (`~/.ssh/id_rsa`, `~/.ssh/id_ed25519`, etc.). Must be kept highly secure with strict file permissions (`chmod 600`).
- Public Keys: Stored on the server in `~/.ssh/authorized_keys` for the corresponding user. Used by the server to verify the client’s identity.
- Host Keys: Unique cryptographic keys generated by the server (`/etc/ssh/ssh_host_*_key`). These are used to identify the server to clients, preventing man-in-the-middle attacks. Clients store known host keys in `~/.ssh/known_hosts`.
The interaction flow generally involves the client attempting a TCP connection on port 22 (by default), the server responding, a secure channel being established (using host keys for server verification), and finally, client authentication. Any disruption at any of these stages can lead to a failed SSH connection.
A Systematic Approach to OpenSSH Troubleshooting
Effective troubleshooting is less about memorizing solutions and more about adopting a logical, diagnostic methodology. The “divide and conquer” principle is paramount: isolate the problem to the smallest possible component. Always start with the most obvious and accessible checks before delving into deeper complexities.
The Diagnostic Mindset: From Broad to Specific
1. Isolate the Scope: Is it just *this* client to *this* server? Or is it all clients to *this* server? Or *this* client to all servers? This helps determine if the issue is client-side, server-side, or network-related.
2. Check the Obvious First: Network connectivity, service status, basic credentials.
3. Consult Logs: Logs are your most valuable resource, offering direct insights into why a connection or authentication failed.
4. Use Verbosity: The `ssh -v`, `ssh -vv`, `ssh -vvv` flags on the client side provide increasingly detailed debugging output.
5. Test Configuration Syntax: Before restarting `sshd`, ensure its configuration is valid.
6. Reboot (as a last resort): While sometimes effective, a reboot doesn’t explain *why* the problem occurred, which is crucial for preventing future incidents.
Unraveling Connection Issues: When the Handshake Fails
The initial hurdle for any SSH session is establishing a network connection. Failures at this stage often manifest as “Connection refused,” “Connection timed out,” or general network errors.
1. Server Not Reachable or Connection Timed Out
This usually indicates a problem before the SSH daemon even has a chance to respond.
Network Connectivity Verification
- Ping Test: Start with a simple `ping `. If this fails, the issue is fundamental network reachability.
- *Solution:* Check network cables, Wi-Fi connectivity, router status, and ensure the server itself is powered on and has network access.
- Traceroute/Tracert: Use `traceroute ` (Linux/macOS) or `tracert ` (Windows) to identify where the connection drops along the network path.
- *Solution:* This helps pinpoint if the issue is local, at an intermediate router, or at the server’s network perimeter. Engage network administrators if intermediate hops are failing.
- Port Scanning (e.g., `nmap`): `nmap -p 22 ` can tell you if port 22 is open and listening.
- *Solution:* If port 22 is closed or filtered, investigate firewalls.
Server-Side Firewall Configuration
Firewalls are the most common culprits for connection timeouts.
- Linux Firewalls (`iptables`, `ufw`, `firewalld`):
- *Check `iptables`:* `sudo iptables -L -n`
- *Check `ufw` (Ubuntu/Debian):* `sudo ufw status`
- *Check `firewalld` (RHEL/CentOS/Fedora):* `sudo firewall-cmd –list-all` or `sudo firewall-cmd –zone=public –list-services`
- *Solution:* Ensure rules permit incoming TCP traffic on port 22 (or your custom SSH port). Example for `ufw`: `sudo ufw allow ssh` or `sudo ufw allow 22/tcp`. Example for `firewalld`: `sudo firewall-cmd –permanent –add-service=ssh` and `sudo firewall-cmd –reload`.
- Cloud Provider Security Groups/Network ACLs: If your server is in a cloud environment (AWS, Azure, GCP), security groups (AWS), network security groups (Azure), or firewall rules (GCP) might be blocking the connection.
- *Solution:* Verify that the security group associated with your server allows inbound TCP traffic on port 22 from your client’s IP address or a sufficiently broad range (e.g., your office IP, `0.0.0.0/0` for testing, though not recommended for production).
2. Connection Refused
This error indicates that the server *received* your connection attempt but actively rejected it. The most common reasons are the SSH daemon not running or misconfigured.
SSH Daemon Not Running
- Check Service Status:
- *Systemd-based (most modern Linux):* `sudo systemctl status sshd`
- *SysVinit-based (older Linux):* `sudo service sshd status` or `sudo /etc/init.d/ssh status`
- *Solution:* If stopped, start it: `sudo systemctl start sshd` or `sudo service sshd start`. If it fails to start, check logs for errors.
- Check Listening Port:
- `sudo ss -tuln | grep 22` (preferred on modern Linux)
- `sudo netstat -tuln | grep 22`
- *Solution:* This confirms if `sshd` is actually listening on port 22 (or your configured port). If nothing is listening, the service isn’t running correctly, or another process is using the port.
Misconfigured `sshd_config`
Syntax errors or restrictive directives in `/etc/ssh/sshd_config` can prevent `sshd` from starting or accepting connections.
- Test Configuration Syntax: `sudo sshd -t`
- *Solution:* This command will parse `sshd_config` and report any syntax errors without attempting to restart the service. Correct any reported issues.
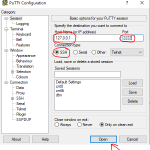
- Port Mismatch: If `Port` is set to something other than 22 in `sshd_config`, your client must specify that port: `ssh -p user@host`.
- `ListenAddress` Restrictions: If `ListenAddress` is configured to listen only on specific IP addresses, and your client is connecting to a different IP, the connection will be refused.
- *Solution:* Comment out or correct `ListenAddress` if it’s too restrictive, then restart `sshd`.
- `AllowUsers`, `DenyUsers`, `AllowGroups`, `DenyGroups`: These directives can prevent specific users or groups from connecting.
- *Solution:* Check if the connecting user is explicitly denied or not explicitly allowed. Temporarily comment them out (with caution) and restart `sshd` to test.
Dissecting Authentication Failures: When You Can Connect, But Not Log In
Once a connection is established, the next hurdle is authentication. This is where most user-facing problems occur, ranging from incorrect passwords to complex key-based authentication misconfigurations.
1. Password Authentication Issues
Incorrect Password or Account Locked
- Double-Check Credentials: The simplest and most frequent cause. Ensure Caps Lock is off.
- User Account Existence and Shell: Verify the user exists on the remote system (`id `) and has a valid login shell (`cat /etc/passwd | grep `).
- PAM (Pluggable Authentication Modules): On Linux, PAM often handles password authentication. Misconfigurations or issues with PAM modules (e.g., `pam_tally2` locking accounts after too many failed attempts) can prevent login.
- *Check PAM logs:* `/var/log/auth.log` or `journalctl -u sshd.service` will often show PAM-related errors.
- *Solution:* Consult PAM configuration in `/etc/pam.d/sshd` and `/etc/security/faillock.conf` (for `pam_faillock`). Unlock accounts using `sudo faillock –user –reset`.
`sshd_config` Directives for Passwords
- `PasswordAuthentication no`: If this directive is set to `no` in `sshd_config`, password authentication is disabled.
- *Solution:* Change to `yes` and restart `sshd`.
- `PermitRootLogin no`: This is a common security best practice. If you’re trying to log in as `root` and this is `no`, it will fail.
- *Solution:* Use a regular user account and then `sudo` for elevated privileges, or temporarily (and dangerously for production) set `PermitRootLogin yes` (not recommended).
- `UsePAM no`: If PAM is disabled, other password validation mechanisms might be in play, or password auth could fail entirely. Ensure it’s `yes` if you rely on PAM.
2. Key-Based Authentication Failures
Key-based authentication is more secure but involves more components, leading to a richer set of potential failure points.
Permissions on Server-Side `~/.ssh` and `authorized_keys`
This is perhaps the *most common* reason for key authentication failures. `sshd` is extremely strict about permissions.
- Home Directory: The user’s home directory (`~`) must not be group-writable or world-writable. `chmod 755 ~` or `chmod 700 ~`.
- `.ssh` Directory: `~/.ssh` must be owned by the user and have permissions `700` (`drwx——`).
- *Solution:* `sudo chmod 700 /home//.ssh` and `sudo chown : /home//.ssh`
- `authorized_keys` File: `~/.ssh/authorized_keys` must be owned by the user and have permissions `600` (`-rw——-`).
- *Solution:* `sudo chmod 600 /home//.ssh/authorized_keys` and `sudo chown : /home//.ssh/authorized_keys`
Incorrect Public Key in `authorized_keys`
- Missing or Malformed Key: The public key (e.g., `id_rsa.pub`) must be correctly copied into `~/.ssh/authorized_keys` on the server, all on one line.
- *Solution:* Carefully copy the *entire* public key from your client’s `id_rsa.pub` (or equivalent) and append it to the `authorized_keys` file. Ensure no line breaks.
- Multiple Keys/Comments: If you have multiple keys, ensure they are on separate lines. Comments are allowed but ensure they don’t interfere with the key string.
Client-Side Private Key Issues
- Incorrect Private Key Path: The client might be trying to use the wrong private key.
- *Solution:* Specify the key explicitly: `ssh -i ~/.ssh/my_private_key user@host`. Check `~/.ssh/config` for `IdentityFile` directives.
- Incorrect Permissions on Private Key: Like public keys, private keys also need strict permissions: `600` (`-rw——-`).
- *Solution:* `chmod 600 ~/.ssh/id_rsa` (or your specific private key).
- Private Key Passphrase: If your private key is passphrase-protected, you’ll be prompted for it. If you enter it incorrectly, authentication will fail.
- `ssh-agent` and `ssh-add`: If you use `ssh-agent` to manage keys, ensure the agent is running and your key has been added (`ssh-add -l` to list loaded keys, `ssh-add ~/.ssh/id_rsa` to add).
`sshd_config` Directives for Public Key Authentication
- `PubkeyAuthentication no`: If this is set to `no`, public key authentication is disabled server-wide.
- *Solution:* Change to `yes` and restart `sshd`.
- `AuthorizedKeysFile`: If this directive is changed from the default (`.ssh/authorized_keys`), `sshd` will look for keys in a different location.
- *Solution:* Verify this path and ensure your public key is in the correct, specified file.
Advanced Diagnostics: Diving Deeper into OpenSSH Issues
When basic checks fail, it’s time to leverage OpenSSH’s built-in diagnostic capabilities and system logging.
1. Verbose Client Output (`ssh -v`, `-vv`, `-vvv`)
Using verbose flags on the `ssh` client is an indispensable first step for deeper diagnostics.
- `ssh -v user@host`: Prints debugging messages about the connection process, authentication attempts, and key exchanges.
- `ssh -vv user@host`: Provides more detail, including cryptographic parameters.
- `ssh -vvv user@host`: Offers the highest level of verbosity, revealing packet exchanges and very granular details.
- *How to use:* Look for specific error messages like “Agent admitted failure to sign using the key,” “Authentication failed,” or details about which authentication methods were tried and why they failed. These messages often directly point to the problem. For example, if it says “Authentications that can continue: publickey,gssapi-keyex,gssapi-with-mic,password”, it tells you what the server is configured to accept.
2. Server-Side Log Files
The SSH daemon logs its activities extensively, providing crucial insights into connection attempts, authentication successes, and failures.
- Linux Log Files:
- `auth.log` or `secure`: On Debian/Ubuntu, SSH logs are typically in `/var/log/auth.log`. On RHEL/CentOS/Fedora, they are in `/var/log/secure`. Use `tail -f /var/log/auth.log` (or `secure`) to monitor logs in real-time while attempting a connection.
- Systemd Journal: On systems using systemd, logs for the `sshd` service can be accessed via `journalctl -u sshd.service -f`.
- Windows (OpenSSH Server): Logs are typically found in `C:ProgramDatasshlogssshd.log` or can be configured for Event Viewer.
- *What to look for:*
- “Failed password for invalid user” or “Failed password for “
- “Authentication refused: bad ownership or modes for directory” (often for `~/.ssh` or `~`)
- “No unencrypted private key loaded”
- “Too many authentication failures”
- “Did not receive identification string” (indicates a non-SSH client or malformed connection attempt)
- Specific PAM errors
3. `sshd` Configuration Testing
Always test your `sshd_config` file after making changes and *before* restarting the service to avoid locking yourself out.
- `sudo sshd -t`: This command performs a syntax check on `/etc/ssh/sshd_config`. If there are any errors, it will report them. No output means the syntax is valid.
- *Solution:* Correct any reported syntax errors. A common mistake is typos in directive names or missing values.
4. Checking SSH Daemon Configuration (Live)
Sometimes, the running `sshd` daemon might not be using the configuration file you think it is, or there might be an override.
- `sudo sshd -T`: This command prints the *effective* configuration of the `sshd` daemon to standard output. This can reveal if a default is in effect that you didn’t expect, or if a global configuration is overriding a user-specific one.
- *Solution:* Compare this output to your `/etc/ssh/sshd_config` to ensure your intended settings are active.
5. Network Interface and Routing Issues
Beyond basic ping tests, deeper network issues can affect SSH.
- `ip a` or `ifconfig`: Verify the server’s IP address and network interfaces are configured correctly.
- `ip r` or `route -n`: Check the server’s routing table to ensure it has a default route and can reach the client’s network.
- *Solution:* Correct any misconfigured network interfaces or routing entries. This might involve editing `/etc/netplan/`, `/etc/sysconfig/network-scripts/`, or using `ip` commands.
Mitigating Specific OpenSSH Error Messages
Certain error messages appear frequently and have specific remedies.
1. “Host key verification failed.”
This occurs when the client’s `known_hosts` file contains a host key for the server that doesn’t match the one presented by the server. This often happens if the server’s host keys have changed (e.g., after a reinstallation) or if a man-in-the-middle attack is suspected.
- *Solution:*
1. If the change is legitimate: Remove the old host key entry from `~/.ssh/known_hosts` on the client. The error message usually tells you which line to remove. `ssh-keygen -R ` is a safer way to do this.
2. If suspicious: Investigate immediately. Do not proceed without verifying the server’s identity through an out-of-band channel.
2. “Too many authentication failures for “
This means the client attempted multiple authentication methods (or multiple keys) and all failed, exceeding the server’s `MaxAuthTries` limit.
- *Solution:*
1. Client-side: Use `ssh -v` to see which keys are being tried. Ensure only necessary keys are loaded into `ssh-agent` (`ssh-add -D` to delete all, then `ssh-add `).
2. Server-side: Increase `MaxAuthTries` in `sshd_config` (temporarily for debugging, as a higher value is less secure) or ensure `PubkeyAuthentication` and other methods are configured correctly.
3. “Agent admitted failure to sign using the key.”
This indicates that `ssh-agent` was running, but when prompted to sign a challenge with a specific private key, it failed to do so (often because the key wasn’t loaded, or the passphrase was incorrect/missing).
- *Solution:*
1. Ensure the key is added to `ssh-agent`: `ssh-add -l` to list, `ssh-add ` to add.
2. If the key requires a passphrase, ensure you’ve provided it to `ssh-add`.
4. “Permission denied (publickey,password,keyboard-interactive).”
This is a general authentication failure message, indicating that none of the methods listed succeeded.
- *Solution:* Systematically check all common authentication failure points:
- Correct password?
- Private key permissions (`600`)?
- Public key present and correct in `authorized_keys`?
- `authorized_keys` permissions (`600`) and ownership?
- `~/.ssh` directory permissions (`700`) and ownership?
- User home directory permissions (`755` or `700`)?
- `sshd_config` settings (`PasswordAuthentication`, `PubkeyAuthentication`, `PermitRootLogin`)?
- Review `ssh -vvv` client output and server `auth.log` or `journalctl` for specific clues.
Best Practices for Preventing OpenSSH Issues
Proactive measures can significantly reduce the likelihood of encountering frustrating SSH problems.
- Consistent Permissions: Always enforce strict permissions (`700` for `.ssh`, `600` for private keys and `authorized_keys`) on both client and server.
- Backup Configuration Files: Before making significant changes to `sshd_config` or `ssh_config`, make a backup. `sudo cp /etc/ssh/sshd_config /etc/ssh/sshd_config.bak`
- Test `sshd_config` Syntax: Always use `sudo sshd -t` after modifying `sshd_config` and before restarting `sshd`.
- Use `ssh-copy-id`: When setting up key-based authentication, `ssh-copy-id user@host` is generally preferred as it handles copying the public key and setting correct permissions on `~/.ssh` and `authorized_keys` automatically.
- Limit `PermitRootLogin`: Disable root login via SSH (`PermitRootLogin no` in `sshd_config`) and use `sudo` for administrative tasks after logging in as a regular user.
- Keep Software Updated: Regularly update OpenSSH client and server packages to benefit from bug fixes and security patches.
- Use Specific Client Configurations: Leverage `~/.ssh/config` on your client to define specific settings for different hosts (e.g., `HostName`, `User`, `Port`, `IdentityFile`).
- Firewall Management: Maintain clear and concise firewall rules, only allowing SSH traffic from trusted IP ranges.
- Regular Auditing: Periodically review `auth.log` or `journalctl` for unusual login attempts or security warnings.
Troubleshooting OpenSSH can initially feel like navigating a labyrinth, but with a structured approach and a deep understanding of its underlying mechanisms, most issues can be resolved efficiently. By systematically checking network connectivity, server configuration, client settings, and authentication parameters, and by leveraging verbose client output and comprehensive server logs, you can pinpoint the root cause of nearly any OpenSSH problem.
Remember, OpenSSH’s robustness relies on careful configuration and adherence to security best practices. Embracing a proactive mindset, regularly reviewing your setups, and understanding the diagnostic tools at your disposal will not only resolve immediate issues but also enhance the overall security and reliability of your remote administration environment. This guide serves as a foundational resource, empowering you to approach OpenSSH challenges with confidence and expertise, ensuring uninterrupted secure connectivity in your technical endeavors.